Planet CCC - Blogs and more around CCC, CCC-Hamburg and Attraktor

November 17, 2026

Netzpolitik.org

Geplante Änderungen der DSGVO: Datenmissbrauch am Arbeitsplatz könnte bald schwerer aufzudecken sein

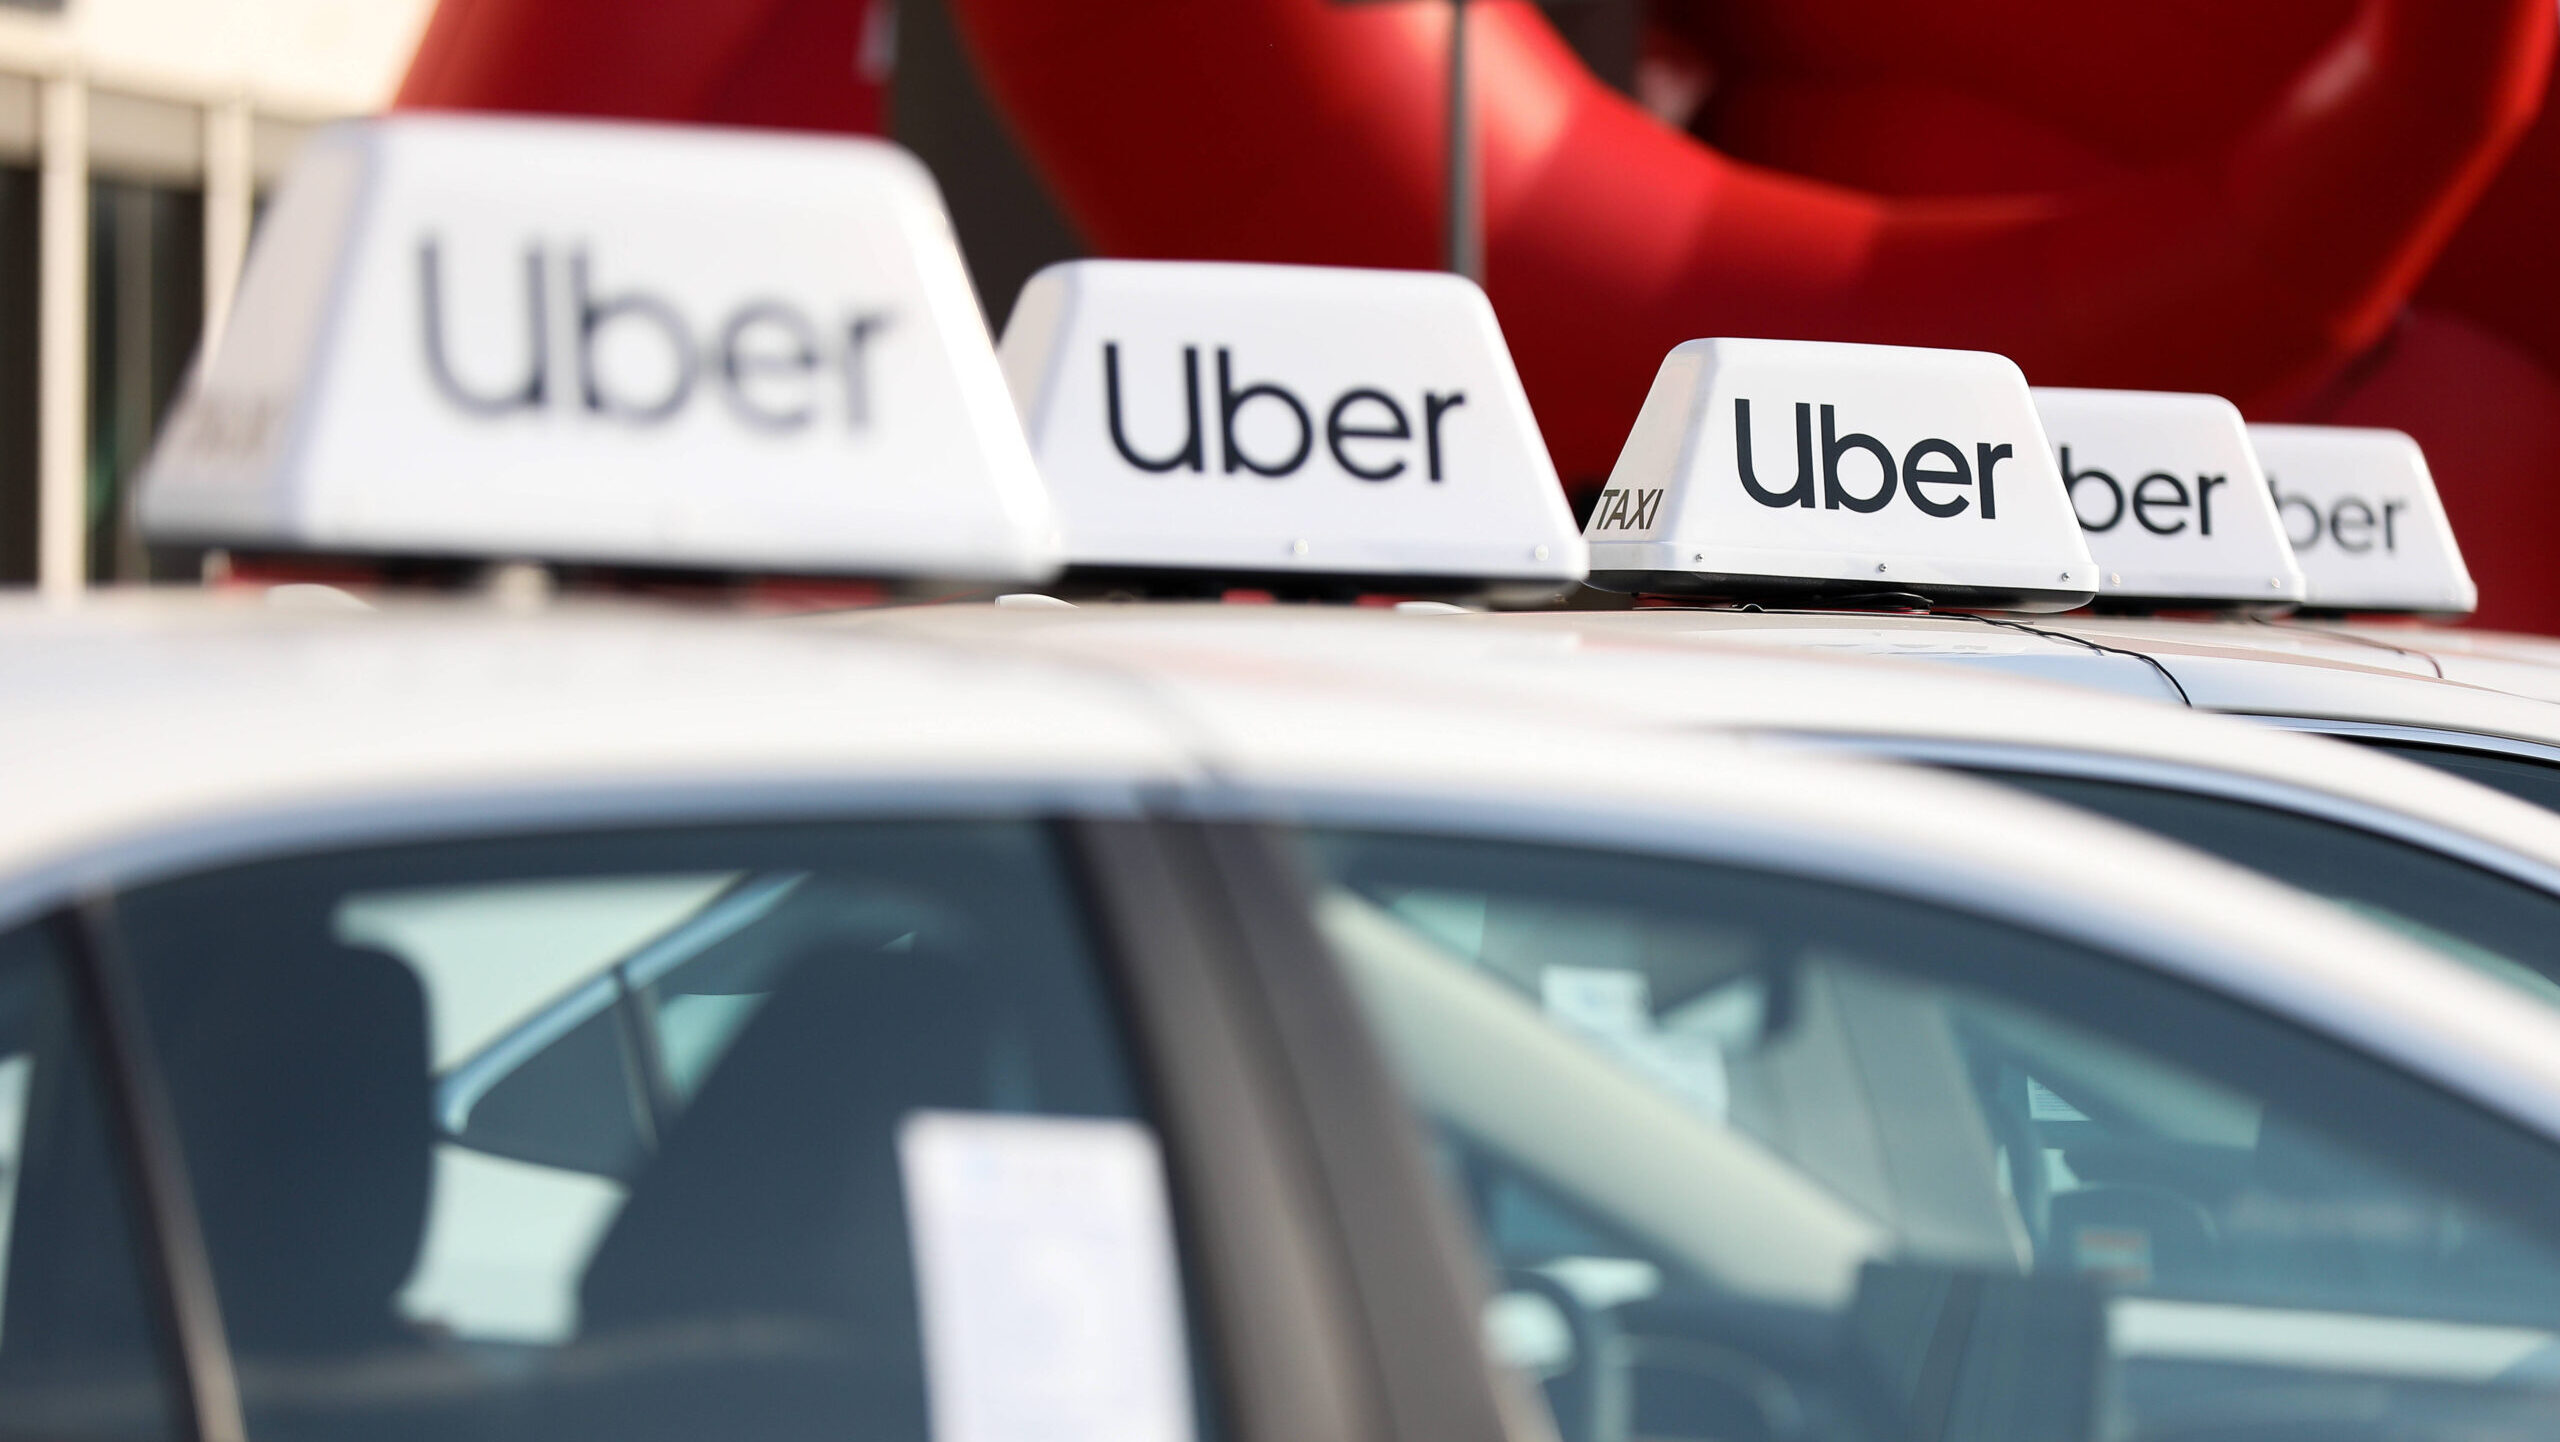
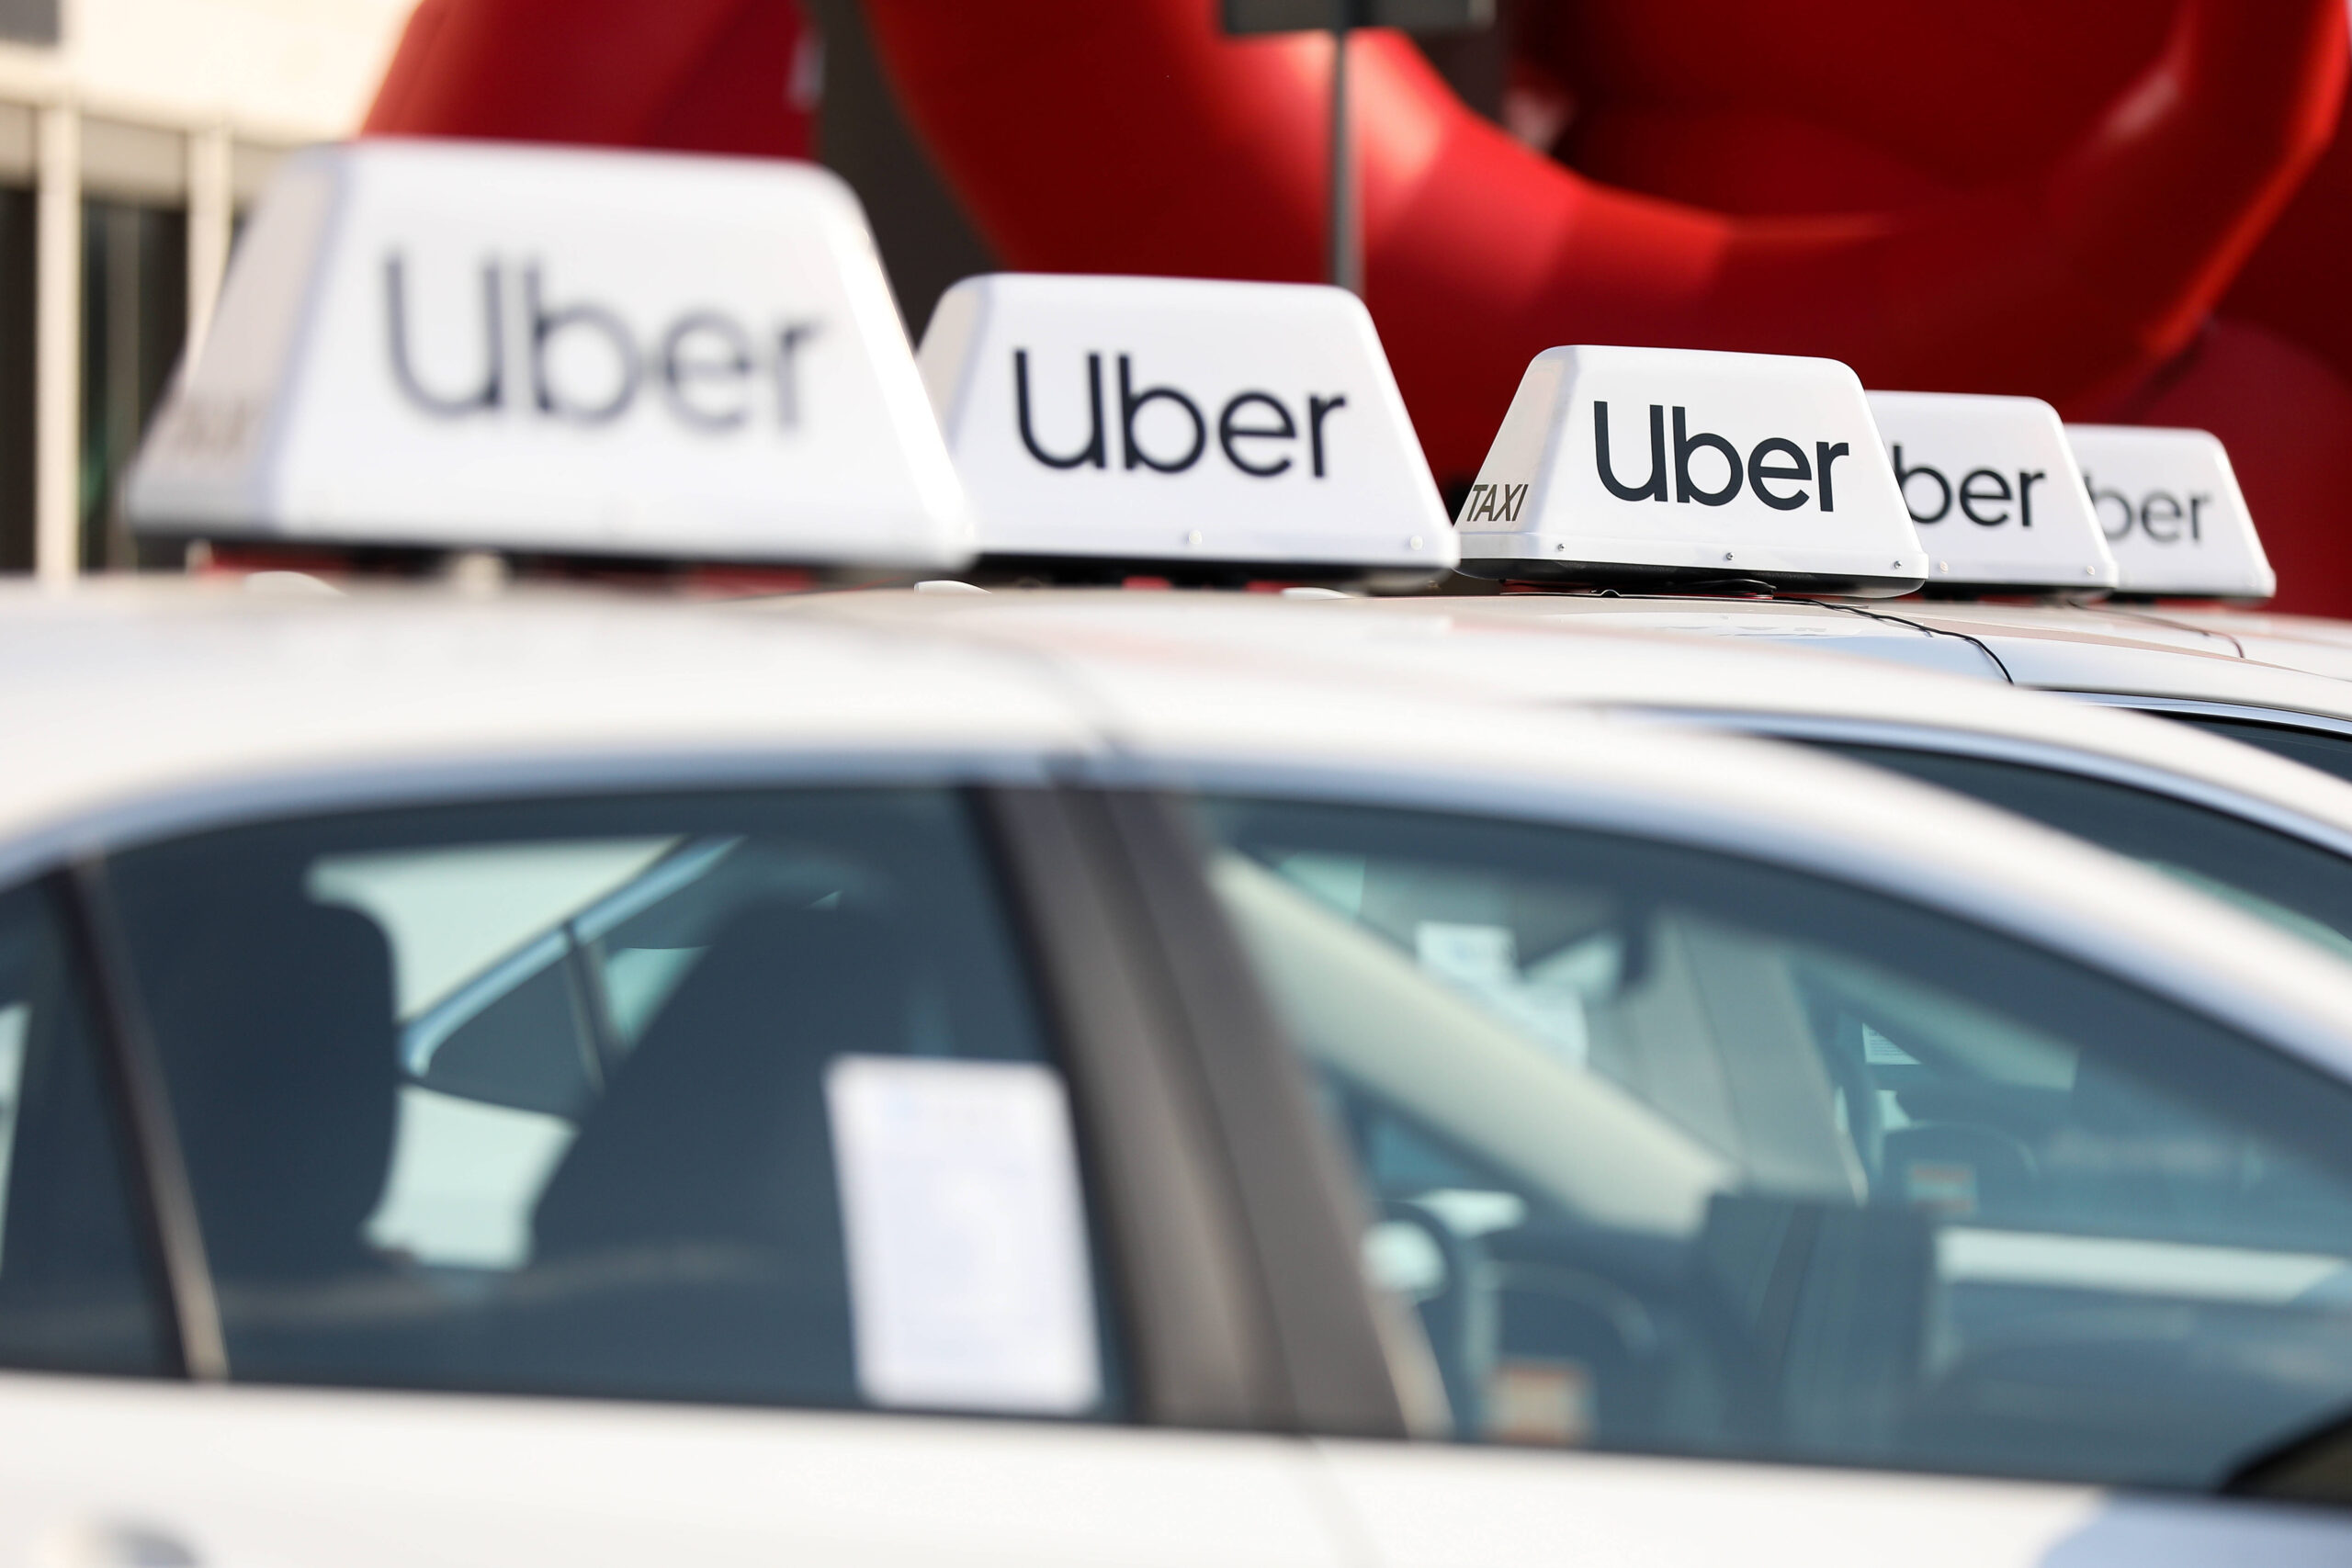
Uber-Fahrer nutzten DSGVO-Datenzugriffsanfragen, um ihre Arbeitnehmerrechte zu verteidigen. – Alle Rechte vorbehalten: NurPhoto via Imago
Die EU-Kommission hat den Digital Omnibus vorgeschlagen, ohne zuvor eine umfassende Folgenabschätzung durchzuführen. Eine Studie des Europäischen Gewerkschaftsinstituts untersucht die möglichen Folgen. Nach Einschätzung der Autoren schwächt der Vorschlag die Datenschutzrechte von Beschäftigten in der EU.

by Muna Turki at November 17, 2026 02:40 PM

Proposed GDPR changes: Workplace Data Abuses Could Soon Be Harder to Uncover

Mehrere Autodächer in einer Reihe auf denen Schilder mit dem Uber-Logo stehenUber Drivers used GDPR data access requests to defend workers' rights – Alle Rechte vorbehalten: NurPhoto via Imago
The EU commission has proposed the Digital Omnibus without conducting a full impact assessment. A study from the European Trade Union Institute examines its potential consequences. The proposal weakens the data protection rights of all workers in the EU, authors say.

by Muna Turki at November 17, 2026 02:38 PM

November 16, 2026

CCC Media

The New Botnet Era: Rethinking Your DDoS Strategy (denog18)

DDoS defense strategies must evolve because modern botnet campaigns combine high-volume, direct-path pressure with stealthier tailored attack components that attempt to overload and evade mitigation systems. In the past, most DDoS attacks were easier for ISPs to identify and block. The hardest cases were botnet-based Layer 7 attacks because they were more difficult to detect and mitigate. Successfully blocking DDoS attacks today requires more than the techniques that worked in the past. Over the past months, botnet size and firepower have increased dramatically. These botnets now drive some of the largest and most effective attacks, not only against individual applications but also against entire network infrastructures, cloud providers, and CDNs. At the end of 2025, we observed record-breaking attacks. This talk explains why we believe those attacks happened, why they continue, and what they reveal about the evolution of botnet-driven DDoS campaigns. Multi-terabit attacks have become much more common, but it is not just the volume of DDoS traffic that is taking down web sites and other targets around the world. The real problem is the tailored, targeted, and dynamic attack components that knock servers offline while remaining below the visibility threshold of many traditional defenses. Today’s large-scale, direct-path attacks increasingly include multiple attack vectors, blending volumetric, state-exhaustion and application-layer components. These botnet-based attacks are designed to overload mitigation capabilities and resources. This talk explains what enabled the expansion of botnets behind today’s attack campaigns and where these new bots are located. For network operators, this matters because these bots now require inbound, outbound, and cross-bound DDoS detection and mitigation. These insights are based on ATLAS, our worldwide DDoS monitoring system. Attendees will leave with a clearer understanding of why botnet-driven DDoS campaigns now demand mitigation strategies that account for visible volumetric pressure and lower-profile attack components at the same time. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/XBCBZT/

Video:denog18-a-98-eng-The_New_Botnet_Era_Rethinking_Your_DDoS_Strategy_sd.mp4

November 16, 2026 11:00 PM

Route Filtering at Scale (denog18)

BGP routing security relies on many technologies, both old and new, such as IRR-based Route Filters and RPKI Technologies like Route Origin Authorizations (ROAs) or Autonomous System Provider Authorization (ASPA-s). While these technologies are well-known, they are still used together, and accurate route filter generation remains a challenging task with significant operational implications for large-scale router filter generation at major tier-1 ISPs. We show that AS-Set documentation in RIR databases is still critical yet systematically overlooked. We evaluate the scope and patterns of these issues - including missing documentation, AS-Set explosive expansion, and cyclic dependencies - demonstrating that accurate AS-Set documentation remains a foundational requirement for operational filtering. We present the toolchain and technologies like Route Query Specification (RQSpec) we use for route filter generation at scale, compensating for the complexity introduced by poor documentation. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/KXMLXN/

Video:denog18-a-97-eng-Route_Filtering_at_Scale_sd.mp4

November 16, 2026 11:00 PM

Ein Jahr DENOG WG Access: Was wir erreicht haben und wo es hingeht (denog18)

Seit unserer Gründung auf der DENOG17 ist ein Jahr vergangen – ein Jahr voller spannender Themen! In dieser Session blicken wir auf die bisherigen Erfolge und Meilensteine der Working Group Access zurück. Gleichzeitig richten wir den Blick nach vorn: Welche Herausforderungen und Projekte stehen im neuen Jahr auf unserer Agenda? Ein kompaktes Update für alle, die auf dem Laufenden bleiben oder die Arbeit der WG zukünftig mitgestalten wollen. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/XMLPRE/

Video:denog18-a-92-eng-Ein_Jahr_DENOG_WG_Access_Was_wir_erreicht_haben_und_wo_es_hingeht_sd.mp4

November 16, 2026 11:00 PM

Network Automation for the Modern Age (denog18)

In the last two decades network automation has gone from a fringe concept reserved for global players to the industry standard at almost every system size. The tooling and concepts have evolved and grown, and an ecosystem has formed and normalized around a few core systems. In this talk, we want to propose a natural next step in the evolution from manual work over templating to driving the system with sources of truth. As the technological and business complexity of networks grows, the data model becomes more and more of a focal point of how we look at the reality of our system. We need to understand our data and our models better than ever before, and make our decisions based on how we model the world, without being constrained by the limits of our pre-fabricated documentation systems. We will speak about what it means for an automation to be driven by your actual data model and how you conceptualize the network, motivated by an actual software system. Over the course of the talk, we will not just talk about concepts, but anchor our ideas in concrete implementation. Nonetheless, this is not a talk about a solution. It’s a talk about an idea and an approach, and, hopefully, the start of a conversation. The talk builds on our previous work and talks around network automation and data modeling. We want to make the case that “source of truth” is a useful step, but not the end state: the more interesting question is whether the model itself can become the driver of automation. The talk will use alembic (https://github.com/cyberwitchery/alembic) as the concrete anchor. We plan to show how a model-first system can represent network concepts, derive operational artifacts, and fit alongside existing DCIM/IPAM/source-of-truth tools without being constrained by their object model. Expected structure: - short history: from manual work to templates to source-of-truth automation - why we end up with our own data model most of the time and what that means - concrete examples from alembic - trade-offs, open questions, and caveats The talk is intended for network engineers, automation engineers, and people maintaining source-of-truth or orchestration systems. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/U3Q97T/

Video:denog18-a-9-eng-Network_Automation_for_the_Modern_Age_sd.mp4

November 16, 2026 11:00 PM

Enjoying BMP with Rotonda in 600 seconds (denog18)

With BMP (BGP Monitoring Protocol) readily available on all major routing platforms, operators have the opportunity to get a view of their networks that's more comprehensive than ever before. Crucially, one needs to collect all this information and make sense of it, ideally without having to invest too much time. In this lightning talk, we present Rotonda, enabling operators to do just that: get started with BMP effortlessly, while providing the scalability and flexibility to monitor any network, any use case. Rotonda is free and open source route collection and analysis software developed by NLnet Labs. We'll introduce BMP, highlight and showcase the main features of Rotonda, and hopefully spark interest to continue the conversation afterwards. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/E7HWCA/

Video:denog18-a-72-eng-Enjoying_BMP_with_Rotonda_in_600_seconds_sd.mp4

November 16, 2026 11:00 PM

Do not look into beam with remaining eye (denog18)

Laser safety is important for everyone, yet knowledge widely differs on what's applicable and and required to do before conducting work on live fibers. This talk will give a brief introduction into laser classes in networking equipment and safety equipment. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/EVWTHX/

Video:denog18-a-40-eng-Do_not_look_into_beam_with_remaining_eye_sd.mp4

November 16, 2026 11:00 PM

IXP Update (denog18)

News from IXPs in Germany As introduced 2021 we collect some parameters from all IXPs, which are active in Germany. This talk aggregates the Updates for all the IXPs in a common format and will be presented in a neutral way. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/LEHAXX/

Video:denog18-a-110-eng-IXP_Update_sd.mp4

November 16, 2026 11:00 PM

DENOG18 Closing (denog18)

It's a wrap! Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/XXSCSP/

Video:denog18-a-105-eng-DENOG18_Closing_sd.mp4

November 16, 2026 11:00 PM

Maybe it is time to consider layer 3 internet exchanges (denog18)

Internet exchanges have presented as shared layer 2 networks for thirty years. I will show the mechanisms that silently blackhole exchange traffic or forward it to the wrong port: missing or incorrect neighbour entries, and unknown unicast flooding. In each case BGP stays established to the route servers and nothing reports a fault. A large exchange stated in writing that it gives no guarantee traffic sent to a peering LAN goes to, and only to, the port of the network it was meant for, and that it knows of no exchange that does. I do not know how many members expect that answer. The rest of the industry has spent years dismantling large layer 2 domains in favour of routed ones. Perhaps it is time for internet exchanges to forward at layer 3, rather than running a layer 2 forwarding domain with a route server making routing decisions. In many cases this needs no new hardware. The switches already used to build exchange fabrics forward at layer 2 and at layer 3 at line rate. Route scale is where careful consideration is needed. The shape of a layer 3 internet exchange switch is already commonplace: each PNI switch a CDN or ISP operates is a routed exchange with several settlement-free peers and one customer on it. Running at layer 3 gives participants complete isolation between ports, the same model that already applies to every other upstream connection that networks buy. RTBH works at the exchange rather than depending on a peer to honour it. Debugging becomes possible from the participant side, because traceroute shows the exchange hop. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/EMHXW7/

Video:denog18-95-eng-Maybe_it_is_time_to_consider_layer_3_internet_exchanges_sd.mp4

November 16, 2026 11:00 PM

Post Quantum Secure Networking (denog18)

Securing our Infrastructure against Cryptoanalysis with Quantum Computers This talk gives an overview of the topic of post quantum cryptography. It explains the problem these algorithms try to solve, shows underlying mechanisms and takes a look at developments of the past few years. The presentation is intended as a summary of the of the topic from a network engineer's point of view: what's going to be on our schedules in the not too distant future? Which solutions are already available, which topics are still under discussion, and what will be required from our infrastructure by industry standards and regulatory bodies? Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/HJXTTT/

Video:denog18-74-eng-Post_Quantum_Secure_Networking_sd.mp4

November 16, 2026 11:00 PM

Carrier-Scale TWAMP Monitoring with DPDK and Commodity x86 Servers (denog18)

Modern telco operators increasingly require continuous active performance monitoring across thousands or even tens of thousands of access nodes. While TWAMP has become the de facto standard for active IP performance measurements, implementing it at carrier scale is far from trivial. This presentation explains how a carrier-scale TWAMP monitoring platform can be built using commodity x86 servers together with DPDK-based userspace packet processing that completely bypasses the Linux networking stack. The talk discusses the architectural decisions required to support massive numbers of concurrent TWAMP sessions, including packet processing, session scheduling, timer management, CPU affinity, NUMA awareness and resource optimization. Real benchmark results and operational experience from large-scale deployments demonstrate the achievable scalability and identify the practical limitations of this approach. Attendees will gain practical insight into designing highly scalable active monitoring systems without relying on proprietary hardware appliances. **Why carrier-scale TWAMP is difficult** Most existing TWAMP implementations are designed for relatively small deployments. Scaling active measurements to tens of thousands of simultaneously monitored access nodes introduces significant challenges in packet processing, timing accuracy, scheduling and resource management. **Why DPDK** The presentation explains why bypassing the Linux kernel networking stack is essential for achieving deterministic latency and high packet processing rates. It discusses how DPDK enables direct NIC access, reduces interrupt overhead and provides predictable packet forwarding performance. **System architecture** Topics include: - Userspace packet processing architecture - DPDK forwarding engine and application-to-engine communication - TWAMP session management - Timestamping offload and packet pacing - Multi-core scalability on commodity x86 hardware **Performance** Real benchmark results will be presented, including: - maximum number of concurrent TWAMP sessions - packets per second - CPU utilisation - memory consumption - scaling across multiple CPU cores - practical deployment limits **Operational lessons learned** The presentation concludes with practical experience gained from deploying large-scale active monitoring systems in carrier environments, including common pitfalls, optimisation techniques and recommendations for future deployments. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/39VKX7/

Video:denog18-49-eng-Carrier-Scale_TWAMP_Monitoring_with_DPDK_and_Commodity_x86_Servers_sd.mp4

November 16, 2026 11:00 PM

A Prosecutor in Another Country Wants Your Data in 8 Hours — Now What? (denog18)

Since 18 August 2026, a prosecutor in another EU country can demand your users' data directly from you — ten days to comply, eight hours if they're in a hurry. No mutual legal assistance, no local court in between: just an order in your inbox and a clock. This talk is the E-Evidence Regulation for the people who actually run the infrastructure: which data you can be forced to produce, how fast, and whether the systems you already operate could even answer in time. A few months in, we'll look at what's working, what's on fire, and what you should have built before the first order arrives. Most coverage of the EU E-Evidence Regulation is written for lawyers. This one isn't. If you operate an ISP, a hosting platform, a cloud, or a registrar, you are the *addressee* of these orders — and the obligations are technical and time-boxed long before they're legal. We'll start with the 90-second operator edition: European Production Orders (EPOC) and European Preservation Orders (EPOC-PR), who can issue them, which data categories are in play (subscriber, traffic, content), and the deadlines that turn this into an on-call problem rather than a policy memo. Then we get to the parts nobody warns you about: that you must designate an establishment or legal representative, that liability is joint and several with fines reaching into a percentage of global turnover, and that there's an actual machine interface behind all this — a decentralised IT system, a transport spec, a hard size limit, and a rollout that may not be finished when the orders start arriving. The practical core is simpler than the crypto-heavy forensics literature suggests. Evidence just needs to be trustworthy: the right data, demonstrably unchanged, anchored in time, and traceable back to where it came from. You don't need a forensics lab for that — you need to know whether the logs and exports you already produce would survive someone asking "how do you know this is genuine?" We'll cover the idea at a level you can act on, then look at how it usually falls apart in practice: data that's already been rotated away, mutable logs, a screenshot instead of a record, no idea who pulled what or when. We close with a field report from the first months of the regime — readiness across the EU, what early orders actually look like, and a pragmatic checklist so that when (not if) one lands in your inbox, you can produce the right data, in a defensible form, within the deadline — without it turning into a fire drill every time. This session is for ISP, hosting, cloud, and registrar engineers, DevOps, abuse/LI-interface teams, and anyone who owns logging or will be the one woken up at 2 a.m. by an 8-hour emergency order. No legal background required; bring your healthy disrespect for bureaucracy. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/J9DJVF/

Video:denog18-42-eng-A_Prosecutor_in_Another_Country_Wants_Your_Data_in_8_Hours_-_Now_What_sd.mp4

November 16, 2026 11:00 PM

SRv6 in the Data Center: Crazy Ideas or Real Use Cases? (denog18)

SRv6 divides opinion — somewhere between visionary promises and the suspicion that it's yet another overly complex protocol the world doesn't need. This talk cuts through both extremes and uses concrete scenarios to show where SRv6 actually delivers today. We start with a compact overview of SRv6 fundamentals: segment types, uSID encoding, and what structurally sets SRv6 apart from MPLS and VXLAN — and when those differences actually matter. Building on that, we examine three practical use cases: routing in the DC fabric (Clos/spine-leaf with BGP underlay), seamless data center interconnect without MPLS overlay complexity, and SRv6 as the transport plane for AI/GPU cluster fabrics with demanding requirements around load spreading and low latency. The throughline: what is production-ready today, what remains theoretical — and where is the added complexity actually worth it? The Goal of this talk is to give a Technology Introduction into SRv6 and how this will be applicable for DataCenter Usecases and compares towards existing Technologies like EVPN/VXLAN. The Goal is to educate the audience about this technology and provide examples of usecases. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/E8TQM8/

Video:denog18-27-eng-SRv6_in_the_Data_Center_Crazy_Ideas_or_Real_Use_Cases_sd.mp4

November 16, 2026 11:00 PM

Quo Vadis IPv6 in Germany? (denog18)

IPv6 deployment is well underway in Germany—some of it visible, much of it happening behind the scenes. So, what’s actually going on? How much progress has the public sector made? Where does our economy stand? And what does having IPv6 at home really means for users? This talk provides an overview of IPv6 deployment across Germany. Here’s a little preview: we’re doing better than you might think. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/G37JXN/

Video:denog18-100-eng-Quo_Vadis_IPv6_in_Germany_sd.mp4

November 16, 2026 11:00 PM

The New Botnet Era: Rethinking Your DDoS Strategy (denog18)

DDoS defense strategies must evolve because modern botnet campaigns combine high-volume, direct-path pressure with stealthier tailored attack components that attempt to overload and evade mitigation systems. In the past, most DDoS attacks were easier for ISPs to identify and block. The hardest cases were botnet-based Layer 7 attacks because they were more difficult to detect and mitigate. Successfully blocking DDoS attacks today requires more than the techniques that worked in the past. Over the past months, botnet size and firepower have increased dramatically. These botnets now drive some of the largest and most effective attacks, not only against individual applications but also against entire network infrastructures, cloud providers, and CDNs. At the end of 2025, we observed record-breaking attacks. This talk explains why we believe those attacks happened, why they continue, and what they reveal about the evolution of botnet-driven DDoS campaigns. Multi-terabit attacks have become much more common, but it is not just the volume of DDoS traffic that is taking down web sites and other targets around the world. The real problem is the tailored, targeted, and dynamic attack components that knock servers offline while remaining below the visibility threshold of many traditional defenses. Today’s large-scale, direct-path attacks increasingly include multiple attack vectors, blending volumetric, state-exhaustion and application-layer components. These botnet-based attacks are designed to overload mitigation capabilities and resources. This talk explains what enabled the expansion of botnets behind today’s attack campaigns and where these new bots are located. For network operators, this matters because these bots now require inbound, outbound, and cross-bound DDoS detection and mitigation. These insights are based on ATLAS, our worldwide DDoS monitoring system. Attendees will leave with a clearer understanding of why botnet-driven DDoS campaigns now demand mitigation strategies that account for visible volumetric pressure and lower-profile attack components at the same time. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/XBCBZT/

Video:denog18-a-98-eng-The_New_Botnet_Era_Rethinking_Your_DDoS_Strategy_hd.mp4

November 16, 2026 11:00 PM

Carrier-Scale TWAMP Monitoring with DPDK and Commodity x86 Servers (denog18)

Modern telco operators increasingly require continuous active performance monitoring across thousands or even tens of thousands of access nodes. While TWAMP has become the de facto standard for active IP performance measurements, implementing it at carrier scale is far from trivial. This presentation explains how a carrier-scale TWAMP monitoring platform can be built using commodity x86 servers together with DPDK-based userspace packet processing that completely bypasses the Linux networking stack. The talk discusses the architectural decisions required to support massive numbers of concurrent TWAMP sessions, including packet processing, session scheduling, timer management, CPU affinity, NUMA awareness and resource optimization. Real benchmark results and operational experience from large-scale deployments demonstrate the achievable scalability and identify the practical limitations of this approach. Attendees will gain practical insight into designing highly scalable active monitoring systems without relying on proprietary hardware appliances. **Why carrier-scale TWAMP is difficult** Most existing TWAMP implementations are designed for relatively small deployments. Scaling active measurements to tens of thousands of simultaneously monitored access nodes introduces significant challenges in packet processing, timing accuracy, scheduling and resource management. **Why DPDK** The presentation explains why bypassing the Linux kernel networking stack is essential for achieving deterministic latency and high packet processing rates. It discusses how DPDK enables direct NIC access, reduces interrupt overhead and provides predictable packet forwarding performance. **System architecture** Topics include: - Userspace packet processing architecture - DPDK forwarding engine and application-to-engine communication - TWAMP session management - Timestamping offload and packet pacing - Multi-core scalability on commodity x86 hardware **Performance** Real benchmark results will be presented, including: - maximum number of concurrent TWAMP sessions - packets per second - CPU utilisation - memory consumption - scaling across multiple CPU cores - practical deployment limits **Operational lessons learned** The presentation concludes with practical experience gained from deploying large-scale active monitoring systems in carrier environments, including common pitfalls, optimisation techniques and recommendations for future deployments. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/39VKX7/

Video:denog18-49-eng-Carrier-Scale_TWAMP_Monitoring_with_DPDK_and_Commodity_x86_Servers_hd.mp4

November 16, 2026 11:00 PM

You Want EGP? You Get EGP! - DENOG Mad Scientist Edition (denog18)

We are all well aware of BGP as our protocol to run the Internet. As we sometimes notice (e.g. in the Talk by Wolfgang Tremmel at DENOG17) BGP still has ties to its predecessor EGP and can still claim it learned things from that protocol (Sometimes for nefarious reasons). Follow me on a journey to find out what we need to do in order to still run the EGP Protocol in 2026. How far back in time do we need to go in order to legitimately put the E into the Origin of BGP updates? Why? Because We do what we must because we can! Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/YUWRSZ/

Video:denog18-43-eng-You_Want_EGP_You_Get_EGP_-_DENOG_Mad_Scientist_Edition_hd.mp4

November 16, 2026 11:00 PM

The Leak-Proof Routing Table: Mastering BGP Roles, ROAs, and ASPA (denog18)

The global routing system was built on a foundation of trust — often exploited by route leaks and hijacks. This session breaks down how a trio of complementary security mechanisms shifts the internet from a model of blind faith to strict verification. We will examine how BGP Roles and the Only-To-Customer (OTC) attribute proactively block leaks multiple hops from the source. Next, we will cover how RPKI Route Origin Authorizations (ROAs) secure the origin point, and how Autonomous System Provider Authorization (ASPA) ensures the entire AS_PATH remains valley-free. Attendees will leave understanding exactly how these tools turn the hope that "BGP speakers behaved" into proof that they did. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/3FWLT7/

Video:denog18-30-eng-The_Leak-Proof_Routing_Table_Mastering_BGP_Roles_ROAs_and_ASPA_hd.mp4

November 16, 2026 11:00 PM

Netzpolitik.org

Wir brauchen jetzt Deine Hilfe: Uns fehlen noch 477.000 Euro!

Wir machen Arbeit, die sonst keiner macht. Dafür brauchen wir deine Unterstützung! Damit wir im kommenden Jahr weiter mit voller Kraft für den Erhalt von Grundrechten und der Demokratie schreiben können.

by netzpolitik.org at November 16, 2026 09:13 PM

Pläne der Bundesregierung: Dutzende Organisationen warnen vor KI bei Migrationsverfahren

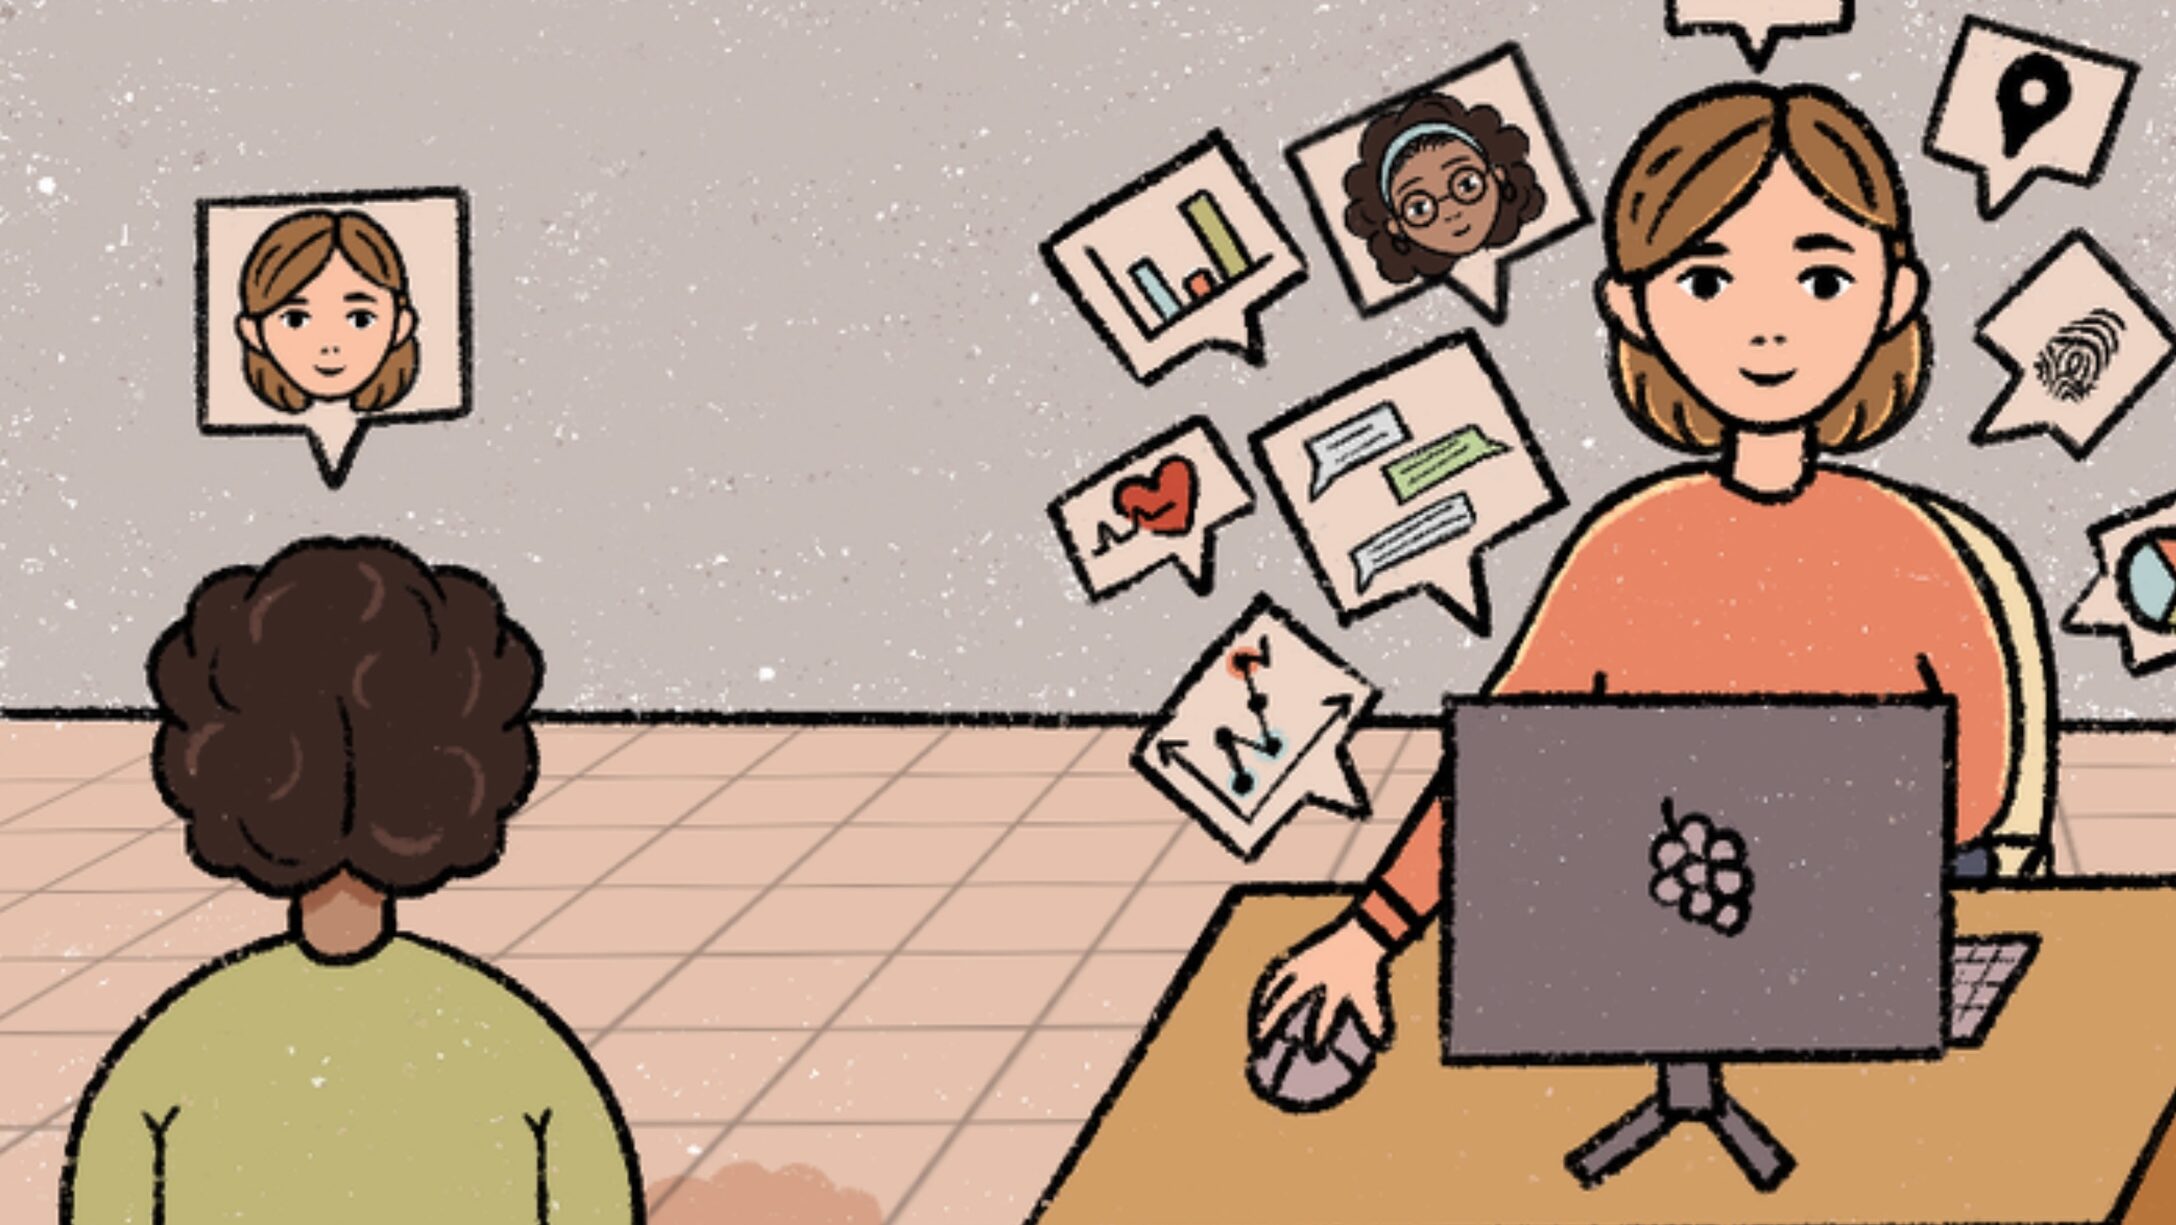
Person mit lockigem Haar steht vor einem Schreibtisch, an dem eine Frau mit kurzem Haar sitzt, umgeben von Symbolen wie Diagrammen, Herz, Chatblasen und Fingerabdruck.Ohne Transparenz der KI-Systeme können sich Betroffene in Migrationsverfahren kaum wehren. (Symbolbild) – CC-BY 4.0: Reihaneh Golpayegani
Wer entscheidet künftig über Asylverfahren: Beamte oder Algorithmen? Der Gesetzentwurf der schwarz-roten Koalition steht in der Kritik. Es mangelt an Datenschutz, Evaluation und Transparenzpflichten, kritisieren Fachleute.

by Markus Reuter at November 16, 2026 04:02 PM

Metalab

Open Social Web Gathering (2026-12-14 18:00:00)

Open Social Web Gathering (2026-12-14 18:00:00)

November 16, 2026 04:00 PM

Netzpolitik.org

Bundeshaushalt: Kein Moos für Open Source

Von wegen ambitionierte Ziele: Bundesregierung investiert wenig Geld in Open SourceNur im Schneckentempo: Wie die Bundesregierung ihre ambitionierten Ziele für Open Source erreicht. – CC-BY-NC-ND 2.0: slackware
Keine Strategie, wenig Geld: Beim Thema Open Source lässt die Bundesregierung ihre Versprechen aus dem Koalitionsvertrag schleifen. Laut Fachleuten wird das besonders im Haushaltsentwurf 2027 deutlich.

by Esther Menhard at November 16, 2026 03:14 PM

UN-Konferenz zu autonomen Waffen: Maschine am Abzug

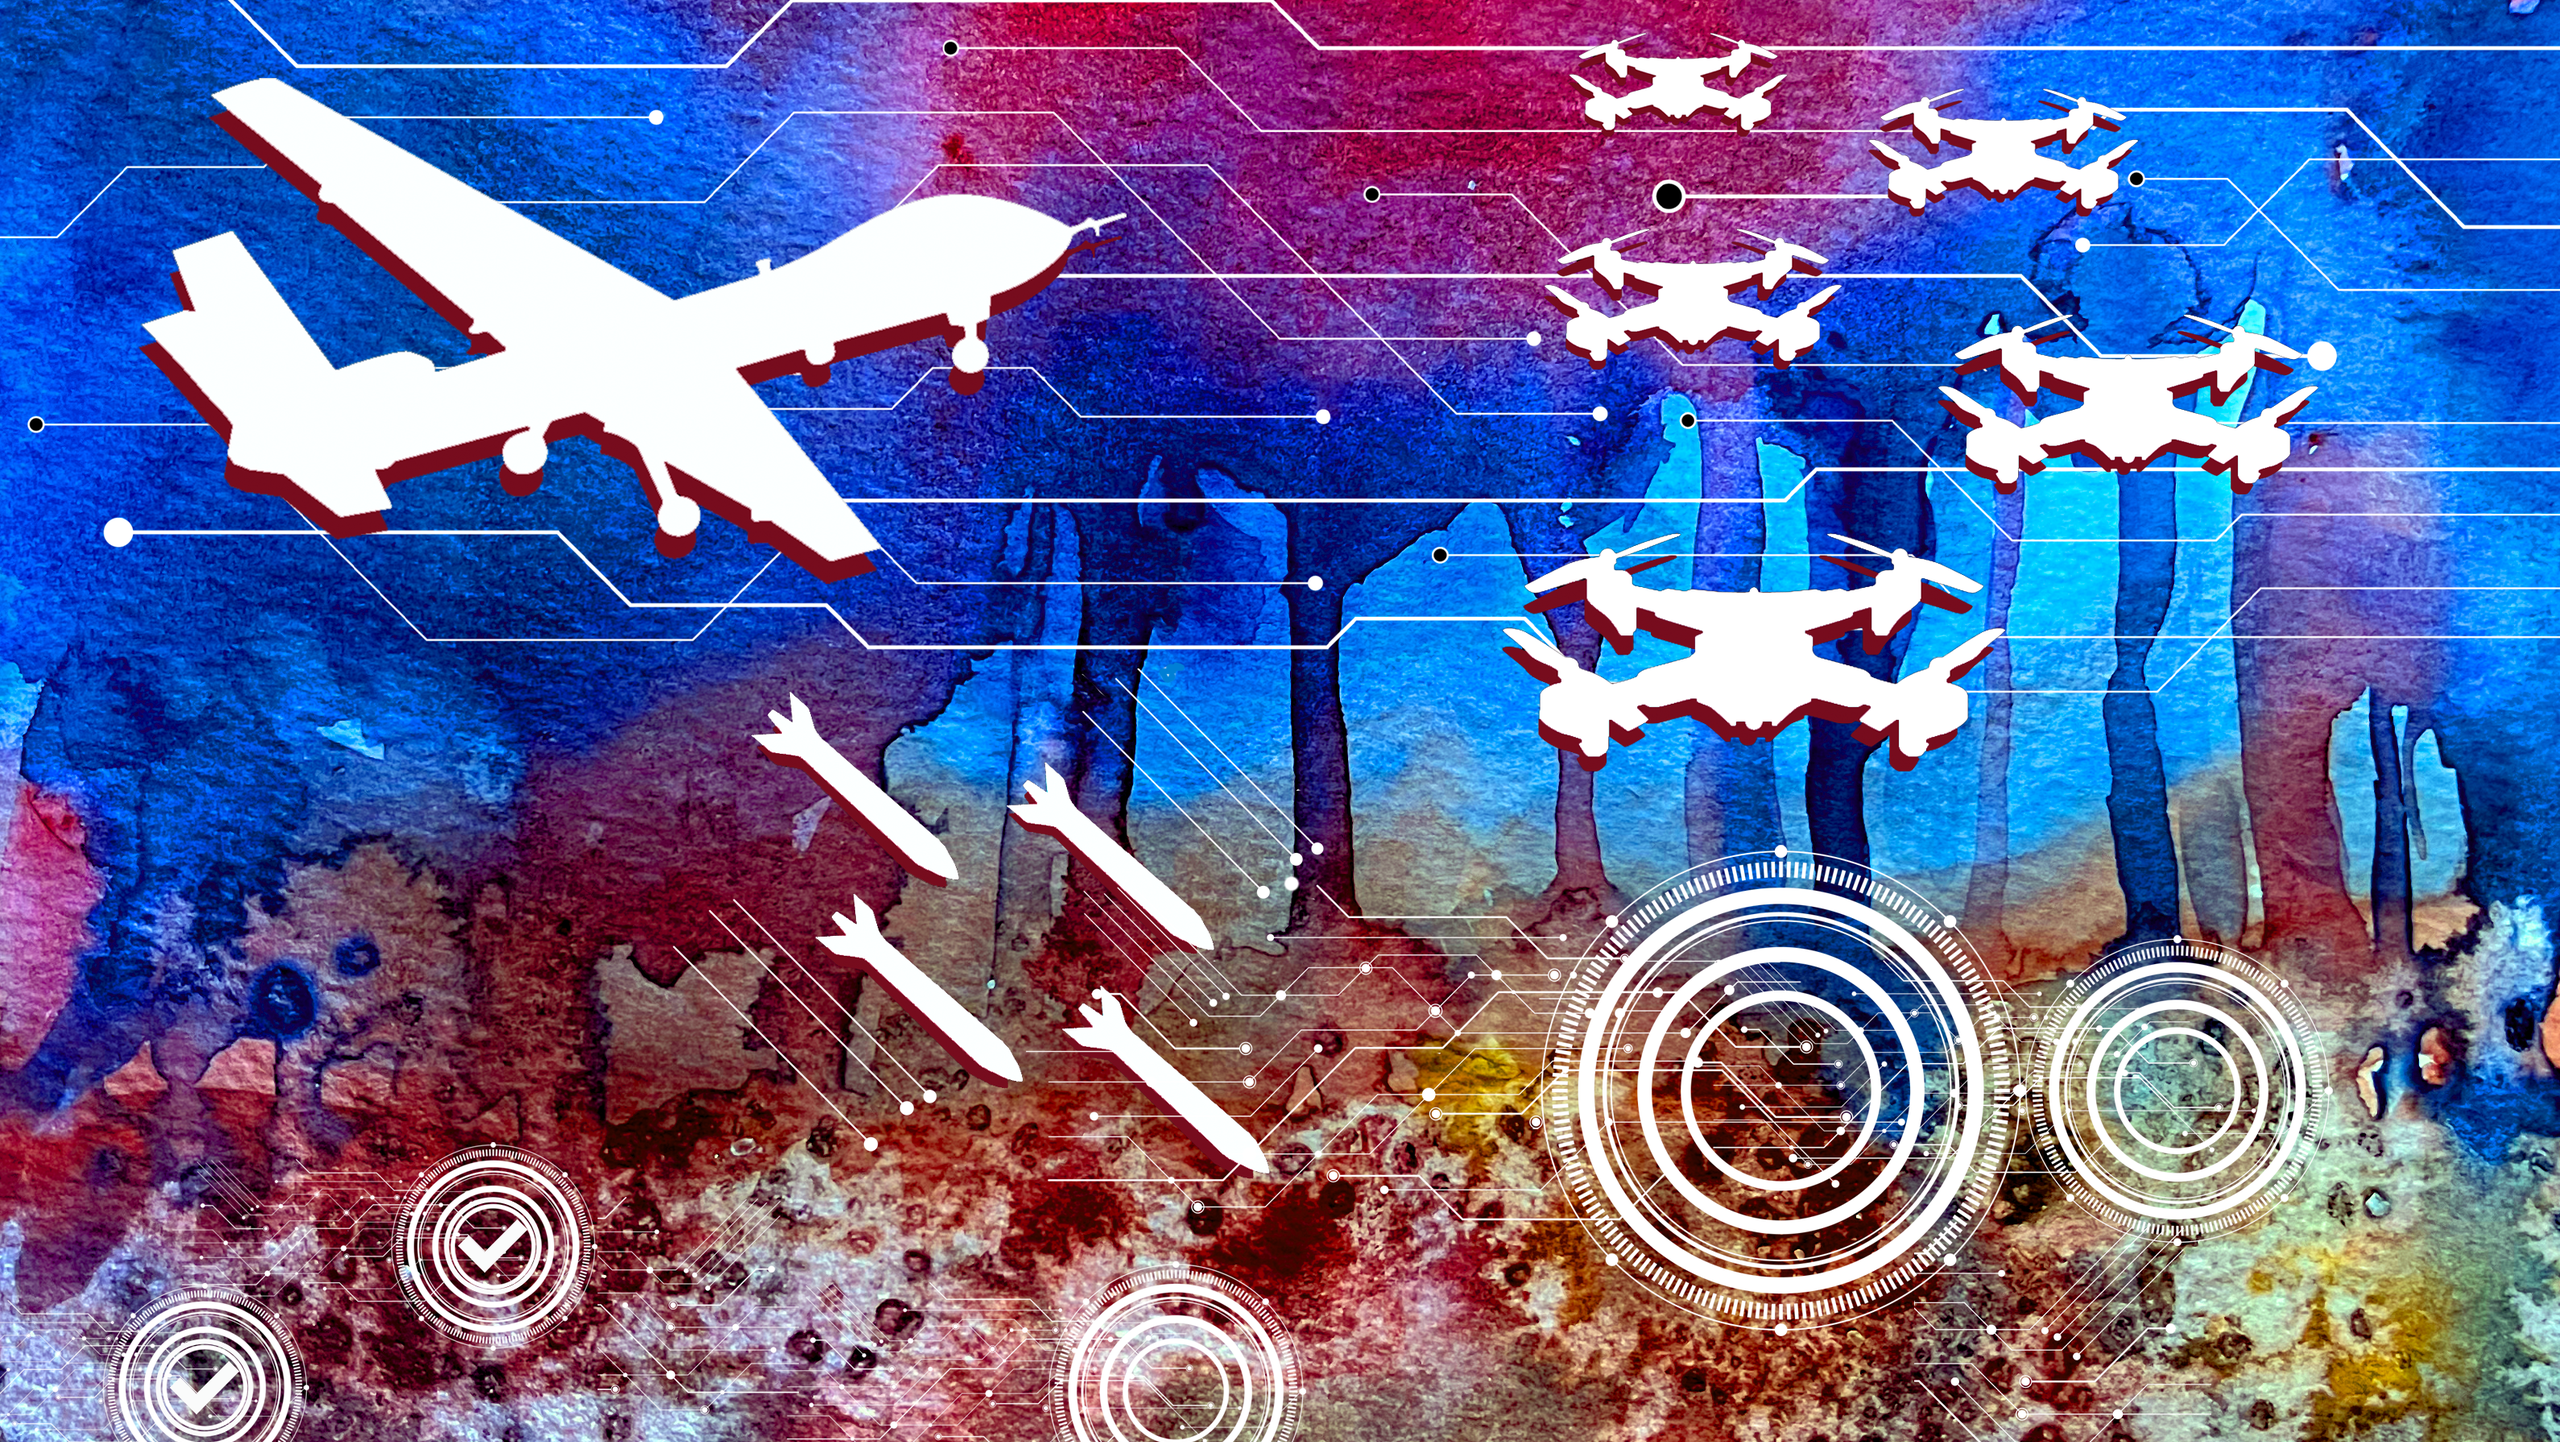
Drohnen, Raketen und ein Flugzeug mit punktförmig markierten Zielen. Weiße Flächen vor Aquarell-Hintergrund in rot-violett.Die Auswahl von Zielen wird immer weiter automatisiert. – CC-BY 4.0: Kathryn Conrad / betterimagesofai.org
In Genf diskutieren Staaten über die UN-Waffenkonvention. Es geht um die vielleicht letzte Chance, automatisiertes Töten zu verbieten.

by Gastbeitrag at November 16, 2026 12:52 PM

November 15, 2026

Metalab

Keymember Workhopp (2026-12-03 18:00:00)

Keymember Workhopp (2026-12-03 18:00:00)

November 15, 2026 11:00 PM

CCC Media

IPv4 as a service on an IPv6-only network (denog18)

Routing IPv4 packets using IPv6 next-hops has been around for some time now. It offers great opportunities to reduce IPv4 address usage in the distribution and access layer, and enables providing IPv4 as a pure add-on, keeping a clean IPv6 address structure underneath. Despite its benefits, major challenges for deploying IPv4-with-IPv6 next-hops in practice persist. While, e.g., BGP supports such routes using RFC8950, many other IGPs still lack support. Other major issues are 'the last mile', i.e., auto-configuring clients (or, for this use-case, more likely servers), and the impact of IPv4-with-IPv6 next-hop usage on traceroutes. In this talk, we will go over some current developments in these areas, which should make IPv4-with-IPv6 next-hops a viable option for practical deployments in the coming years. We will also expand further on possible deployment scenarios, where IPv4-with-IPv6 next-hops can remove further legacy Layer-2 infrastructure, e.g., LACP. What actually changes in your network when you stop treating IPv4 as infrastructure and start treating it as a service? draft-vanmook-intarea-ipv6-resolved-gateway (presented at IETF 126, WG adoption call pending) defines a single sentinel gateway address, provisionally 192.0.0.11 (requested from the IANA Special-Purpose Registry, not yet assigned), handed out as the ordinary DHCPv4 default gateway. Updated hosts resolve their first hop from the IPv6 neighbour cache; unmodified hosts ARP for the sentinel once and the router answers. That's the whole mechanism. Everything downstream of it is the interesting part. This talk is about what that does to a running network: no IPv4 subnets anywhere, no ARP, no FHRP, IPv4 address pools that go flat — any /32 works anywhere in the footprint, nothing stranded by subnet sizing. The core forwards v4-via-v6 (RFC 8950) with no IPv4 configured on any router interface. On the implementation side: host implementations for Linux (userspace daemon and native systemd-networkd), FreeBSD, macOS and Windows, with prebuilt packages; a namespace conformance lab with a zero-ARP assertion; verified unmodified-host behaviour across seven operating systems; and vendor configuration examples for IOS XR, JunOS, SR OS, EOS and RouterOS. On the router side, three working deployment models: a single-gateway reference, an active/active anycast VRRP pair, and a BGP-orchestrated multi-gateway fabric — fungible gateways, host /32s injected from inventory, and the entire DHCPv4 path carried as IPv4 values over IPv6 next-hops, with no IPv4 management network at all. Plus the failure modes, the ND health prerequisites, and what breaks when you get it wrong. No tunnels. No translation. No flag day. Keep the shape, change what it means. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/V7Y3X9/

Video:denog18-a-99-eng-IPv4_as_a_service_on_an_IPv6-only_network_sd.mp4

November 15, 2026 11:00 PM

Teach Networking!? (denog18)

There are many ways for career starters to get into IT: apprenticeships, university degrees, dual study programs, or through self-study. But how do they learn networking and IT infrastructure? With this lightning talk, I’d like to inspire you to teach young people how networking works! What are the most difficult topics to explain? What about practical experience? I've been teaching the basics of networking for several years now, and I'd like to share my experience with you. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/E7UDUC/

Video:denog18-a-94-eng-Teach_Networking_sd.mp4

November 15, 2026 11:00 PM

EVPN for humans (denog18)

EVPN is everywhere, be it datacenter, service provider or campus - and every vendor says you need it. But EVPN rightfully has a reputation problem. It is rarely truly understood, even by vendors themselves, and often treated as a black box. The RFCs read like tax law, and the quality of vendor documentation doesn’t help either. This talk aims to be nothing less than a gentle introduction and a deep dive into EVPN at the same time. We‘ll explore the abstract concepts and frequently misused terminology in order to build an intuitive mental model. We will also look into the often overlooked origins of EVPN, which explain many of its design decisions and behaviours. Finally, we’ll take a look at tricky mechanisms like Anycast Gateways and Multihoming, so your next EVPN debugging session doesn’t become another unplanned nightshift. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/YTBLUH/

Video:denog18-a-93-eng-EVPN_for_humans_sd.mp4

November 15, 2026 11:00 PM

IPv6 routing loops -- A call to fix router configurations. (denog18)

Routing loops and the amplification of looping packets are known problems on the IPv6 Internet. In a recent measurement study, we found that both problems are still present, potentially harming Internet stability. Although routing loops are often easy to fix, they receive limited attention from the network operator community. Since 2025, we aim to raise awareness of routing loops and amplification at network operator events. In 2026, we started to weekly measure the deployment of routing loops and amplifications on the IPv6 Internet. In this talk, we present how community outreach has helped significantly reduce the impact of these network misconfigurations. We further provide an update on the current state of these issues on the IPv6 Internet with a particular focus on the RIPE and DE region. We hope these misconfigurations will eventually disappear and encourage the DENOG community to spread the word, check their networks, and help eliminate routing loops from the IPv6 Internet. Until then, we will continue measuring, reporting, and raising awareness. To assist in resolving these problems, we have made our findings publicly available at https://ipv6-sra.realmv6.org/routingloops, allowing operators to check whether their networks are affected by routing loops. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/PRRFUN/

Video:denog18-a-85-eng-IPv6_routing_loops_--_A_call_to_fix_router_configurations_sd.mp4

November 15, 2026 11:00 PM

ICMP trickery in "reduced-IPv4" networks (denog18)

Did you think IPv6 transition technologies were too easy? "one more" wasn't enough choices? Did you ever have to debug one of these "simple" setups? Come join for a walk through ICMP (v4 and v6) behavior and features! This presentation will go through the various edge cases and overlaps between ICMPv4 and ICMPv6 in transition/IPv4 phase-out setups. One of these is likely applicable to most of us — hopefully you're not a poor soul for whom _all_ apply! A rough outline: - RFC 4884 and historic context: ICMP in MPLS networks - convincing your tools to not hide the goods from you - ICMP translation in NAT64 devices - midpath ICMPv6 into NAT64 - 192.0.0.8 is love, 192.0.0.8 is life - ICMPv4 on RFC 8950 devices - Good thing nobody needs PMTUD, right? Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/ZQEANK/

Video:denog18-a-84-eng-ICMP_trickery_in_reduced-IPv4_networks_sd.mp4

November 15, 2026 11:00 PM

QoE-riosities of 2026 - What we saw on the Internet this year (denog18)

While everyone talked about the DENIC outage this year, we monitored the critical stuff higher up the stack. The football world championship was a challenge for streamers and network operators. So, how did they actually perform under pressure? Beyond live events, we put different access technologies to the test in our lab to analyze how factors like latency, jitter, and bandwidth caps directly impact Quality of Experience (QoE) on the web and beyond. Let's have a data-driven look at the Unexpected of 2026. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/ZCXTKW/

Video:denog18-a-68-eng-QoE-riosities_of_2026_-_What_we_saw_on_the_Internet_this_year_sd.mp4

November 15, 2026 11:00 PM

Retrofitting API into a routing software (denog18)

Configuring a router via text CLI and configuration file editing is not very 2026. In BIRD, we are trying to catch the departing train and implement a CORECONF variant of an IETF-standardized YANG-based API. We've created a prototype but getting things right is harder than it seems. This is a report on what has already gone wrong and what is expected to fail in the future. While a standardized API looks simple on surface, the reality is much more convoluted. There are three standards for communication, NETCONF, RESTCONF and emerging CORECONF, each of these with slightly different semantics. Lots of the YANG modules are not yet finalized and implementation specifics are leaking into them from their authors. In the best case, we end up with the implementations slightly differing in what is implemented, and being mostly compatible for automated access. Yet, the actual future may be much more dire, with the users having to cater for three different protocols and vastly diverse implementation status of the standardized API. All of that is spiced up by performance challenges. With BIRD, we are kinda late to the party. Everybody has some API working. That brings a disadvantage on the market, but it also allows us to study the previous attempts, see possible problems and implement our API to our standards, including high performance and stability. We can also see emerging compatibility issues and there are some attempts to develop proxies and convertors to bridge the gaps. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/3BJJKY/

Video:denog18-a-51-eng-Retrofitting_API_into_a_routing_software_sd.mp4

November 15, 2026 11:00 PM

EVPN - One Control Plane to Rule Them All (denog18)

Modern service provider networks are evolving rapidly: transports like VXLAN, MPLS, Segment Routing and SRv6 are being used while many legacy control plane protocols are still in operation. This often results in unnecessary complexity, multiple signalling mechanisms and operational overhead. In this talk, I’ll explore how BGP EVPN has evolved into a transport-agnostic control plane capable of unifying services across MPLS, VXLAN, SR, and SRv6. The goal is simple: move away from fragmented legacy protocols and toward a single, scalable control plane for L2 and L3 services. We’ll look at recent EVPN innovations and discuss how service providers can benefit from simplifying their architectures while preparing their networks for future transport technologies. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/VCQLXW/

Video:denog18-a-45-eng-EVPN_-_One_Control_Plane_to_Rule_Them_All_sd.mp4

November 15, 2026 11:00 PM

Day 1 Closing (denog18)

That's a wrap on Day1, time for the social! Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/EQ7KVJ/

Video:denog18-a-106-eng-Day_1_Closing_sd.mp4

November 15, 2026 11:00 PM

DENOG18 Opening (denog18)

Welcome to DENOG18! Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/UB3PVV/

Video:denog18-a-104-eng-DENOG18_Opening_sd.mp4

November 15, 2026 11:00 PM

Ethernet Won Inside the AI Data Center. Can It Cross an Operator Boundary? (denog18)

Inference is quietly overtaking training as the dominant AI workload, and unlike training — concentrated in a handful of hyperscale halls — inference wants to sit close to users, pulling AI capacity into distributed sites across Europe. The industry has spent the last two years re-engineering Ethernet (via the Ultra Ethernet Consortium and platforms like NVIDIA Spectrum-X) to match InfiniBand's performance for exactly this kind of workload, and now even ships Ethernet fabrics purpose-built to stitch multiple physical data centers into one logical AI factory. That's a solved problem when one company owns every site. This talk asks what happens when it isn't — when distributed inference has to span operators, jurisdictions, and ownership boundaries — and what a federated, policy-aware Ethernet fabric for that world would need to look like. Ethernet is rapidly becoming the preferred back-end network for AI infrastructure. Technologies such as RoCE, Ultra Ethernet, NVIDIA Spectrum-X, and emerging “scale-across” architectures promise predictable, high-performance connectivity within and between AI data centers. These architectures generally make one important assumption: a single organization controls the servers, switches, telemetry, congestion policies, and inter-site connectivity. Under that model, several physical data centers can be engineered to behave as one logical AI environment. Distributed European AI infrastructure may not have that luxury. Inference capacity will increasingly be deployed across hyperscalers, regional clouds, colocation facilities, metro-edge sites, and specialist GPU providers. The networks connecting those sites may also belong to different fiber and connectivity operators. Each participant controls only part of the infrastructure, exposes limited operational information, and may operate under different commercial and jurisdictional requirements. This creates a question that faster Ethernet alone cannot answer: what happens when an AI fabric reaches an operator boundary? The talk begins by separating two ideas that are frequently conflated. Distributed AI services can steer requests between independent sites without extending a tightly coupled GPU fabric between them. Some workloads, however, including model distribution, distributed inference, resilience between GPU sites, and certain forms of model parallelism, place much stronger demands on inter-site connectivity. We will examine which workloads genuinely benefit from network-level federation and which should remain distributed at the application layer. We will then look at what changes when traffic crosses a network-to-network interface. Can congestion-control assumptions survive between independently operated domains? What latency, loss, and bandwidth guarantees are technically credible? How can operators exchange useful telemetry without exposing internal topology? Who selects the end-to-end path, who responds to failures, and how can customers verify that the delivered service matches what was promised? Sovereignty adds another dimension to this problem. A sovereign AI service is not defined solely by the location of its GPUs. Customers may also care about where their traffic travels, who owns and operates the infrastructure, which jurisdictions can exercise control over it, where encryption keys are held, and whether those claims can be independently verified. Consequently, path selection may need to consider geography, jurisdiction, operator identity, and operational control alongside conventional performance metrics. The talk proposes a candidate architecture based on coordinated path computation with domain-local enforcement. Each operator retains control of its own network while exposing an abstract set of capabilities such as latency class, available bandwidth, path diversity, geographic scope, and jurisdictional attributes to a higher-level coordinator. The coordinator requests an outcome rather than configuring another operator’s network, while end-to-end measurement verifies whether the resulting service meets its performance and sovereignty objectives. We will test this architecture against the timing and congestion requirements of GPU networking and identify where conventional carrier federation begins to fail. The goal is not to claim that a continent-wide lossless Ethernet fabric is immediately practical. It is to determine which multi-operator AI connectivity services are feasible, which workloads they can support, and which technical assumptions still require new standards or experimentation. Attendees will leave with: - A clear distinction between distributed inference services and distributed GPU fabrics. - An understanding of what breaks when AI traffic crosses an operator boundary. - A practical definition of sovereignty covering compute, connectivity, control, and verification. - A candidate model for policy-aware, multi-operator AI connectivity. - A framework for identifying which AI workloads can realistically operate across federated networks. The commercial opportunity for operators may not be “one enormous Ethernet fabric.” It may instead be something more achievable: verifiable, policy-aware connectivity between AI-capable sites, with measurable performance, geographic, jurisdictional, and operational guarantees. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/73Q8NL/

Video:denog18-90-eng-Ethernet_Won_Inside_the_AI_Data_Center_Can_It_Cross_an_Operator_Boundary_sd.mp4
November 15, 2026 11:00 PM

You can't make everybody equally happy - Measuring Anycast with AI as the Third Member of a Two-Person Team (denog18)

Anycast is easy to explain and notoriously difficult to observe. Announce the same IP address from multiple locations, allow BGP to choose a path, and traffic should reach the "nearest" instance, although BGP's idea of nearest often has little to do with geography. ProVision (formerly 6connect) operates an anycast DNS platform spanning six prefixes, 39 BGP nodes, 13 regions, and five continents. For years, we knew the platform worked because queries were answered. What we could not prove was how it worked: which users reached which nodes, how quickly packets arrived, and where traffic quietly disappeared. This presentation tells the story of how we turned one of anycast's most frustrating behaviors-ICMP replies returning to the "wrong" node-into a measurement. That insight grew into an automated pipeline running 117,000 probes per second across 2.6 million targets, measuring latency, loss, jitter, routing behavior, path MTU failures, ECMP paths, and visibility at 845 Internet Exchanges. It is also the story of how two network engineers who are not full-time developers built the system through intensive collaboration with AI coding models. AI supplied much of the implementation capacity; the humans supplied decades of network intuition, architectural direction, validation, and the authority to say when the code was confidently wrong. Anycast underpins critical Internet services, including DNS, content delivery networks, and DDoS mitigation platforms. The model appears simple: announce the same IP address from multiple locations and allow BGP to direct traffic toward the best available path, but the operational reality is far less transparent. ProVision (formerly 6connect operates an anycast DNS platform built around six prefixes announced by 39 BGP nodes in 13 regions across five continents. The platform answered queries reliably, yet ordinary service monitoring could reveal only part of the story. It could tell us that a DNS request succeeded, but not always which node handled it, whether BGP selected the node we expected, how latency differed across the catchment, or where packets were being lost without causing a visible outage. Measuring the network from inside the platform created a chicken-and-egg problem. Anycast is designed to make many distributed instances appear to be one destination, so the topology we wanted to study was the same topology the service was designed to conceal. We could not simply ask the Internet which node it would reach. We needed a way to make the network reveal its own routing decisions. The breakthrough came from a behavior that initially appeared to undermine the measurements. We sent probes from the production anycast source addresses and observed that ICMP errors frequently returned to the "wrong" node rather than the node that originated the probe. That wrong node was the answer. The node receiving the ICMP response was the node BGP had selected as the return path for the router generating it. By recording those responses across the network, we could begin mapping real anycast catchments from the perspective of the infrastructure itself. The apparent flaw became the core measurement primitive. From that insight, we built a fully automated daily measurement pipeline capable of: Running 117,000 probes per second across 2.6 million targets Measuring round-trip time, packet loss, and jitter for 1.4 million addresses Detecting path MTU discovery black holes Performing ECMP-aware traceroutes Correlating active measurements with BGP monitoring Measuring platform visibility at 845 Internet Exchanges Attendees will leave with a practical understanding of why anycast is so difficult to measure, how asymmetric ICMP routing can reveal real BGP catchments, and what it takes to turn that observation into a large-scale monitoring system. They will also see a grounded example of AI-assisted engineering in which coding models expanded the capacity of a very small team without replacing the network judgment required to build something trustworthy. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/MRZYPH/

Video:denog18-82-eng-You_cant_make_everybody_equally_happy_-_Measuring_Anycast_with_AI_as_the_Third_Member_of_a_Two-Person_Team_sd.mp4

November 15, 2026 11:00 PM

Geoinformation Systems & Internet Infrastructure (denog18)

KML, KMZ, DXF - hat wahrscheinlich schon jede:r mal in der Hand gehabt, nach dem man redundante Leitungen bestellt hat. Aber was macht man eigentlich sinnvolles damit? KML, KMZ, DXF - everyone knows or used those file formats, at least after asking the carrier where the redundant circuits are. But is there anything useful you can do with those files? Geoinformationsdaten sind eine der Grundlagen für stabil funktionierende Infrastruktur. Egal ob Glasfasern im Boden, Glasfasern an Hochspannungsmasten oder Richtfunkstrecken. Wie funktioniert die Trassenplanung- und Instandhaltung, und welche Vorteile habe ich als Nutzer:in um meinen Netz zu verstehen und den Netzbetrieb zu optimieren? Geo information data are the basis for reliable infrastructure. Not only for fiber in the ground, but even fiber on power lines or microwave links are planned this way. How does the planning of new fiber routes and their maintenance work, and which benefits do I get from geo data for my own network? Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/97DCW3/

Video:denog18-61-eng-Geoinformation_Systems_Internet_Infrastructure_sd.mp4

November 15, 2026 11:00 PM

IPv6 in firmware: Still booting in the wrong decade (denog18)

Every server depends on firmware to boot and most also rely on firmware for remote management. U-Boot, EDK2 (UEFI), OpenBMC, you name it. And they all share the same issue: IPv6 support ranges from half-baked to non-existent. Why is this still the case in 2026? In this talk I'll go into two areas of server firmware that operatores rarely look at closely: the one that boots the server, and the one that allows out-of-band management via the Baseboard Management Controller (BMC). On the boot side: Do PXE and HTTP boot actually work over IPv6? And what unexpected side effects do you might see? On the management side: How does IPv6 support look on a BMC today, and what's still broken? Nobody's going to fix what nobody complains about. Let's find out how broken this is and what we can do about it. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/XPH3W7/

Video:denog18-54-eng-IPv6_in_firmware_Still_booting_in_the_wrong_decade_sd.mp4

November 15, 2026 11:00 PM

Modular Nokia SR OS automation from scratch (denog18)

Existing automation solutions are usually monolithic and require you to migrate all of your existing infrastructure at once to the automation. I wanted to introduce automation step by step and wanted to continue to use our existing sources of truth. So I have built a modular automation solution that allows us to build a completely separated automation module for everything we want to automate in our network. Existing automation solutions are usually monolithic and require you to migrate all of your existing infrastructure at once to the automation. But I wanted to continue using our existing sources of truth and wanted to introduce automation in our network step by step and not in one big step. Additionally, there is the security perspective: do you really want to grant an automation solution that you don't fully understand internally unrestricted access to all of your routers? The solution: modular network automation from scratch: write a module for any aspect you want to automate in your network. Want to automate your peerings with Peering-Manager? Write a module for it. Want to automate your base router interfaces with NetBox? Write a module for it. The modules itself are isolated from each other in the configuration by using one config group for each module (basically a separate config tree for each module). This by design eliminates the possibility of collisions between modules and makes consecutive deployments easier by fully replacing the config group on each run. It additionally allows you to minimize the permissions of an automation user to the absolute required minimum by only granting them access to the config group. Furthermore, the use of config groups allows you to override the automation on any given time in the main config tree or even exclude some parts of the main config tree from it. Although this solution was developed for Nokia SR OS, it can in principle be extended to any platform that is transactional and supports something like config groups. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/KPYWEU/

Video:denog18-50-eng-Modular_Nokia_SR_OS_automation_from_scratch_sd.mp4

November 15, 2026 11:00 PM

Newcomer Sessions (denog18)

Welcome to your first DENOG conference. In this session, we will guide you through the community, the event and everything DENOG! Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/AVHF39/

Video:denog18-109-eng-Newcomer_Sessions_sd.mp4

November 15, 2026 11:00 PM

IPv4 as a service on an IPv6-only network (denog18)

Routing IPv4 packets using IPv6 next-hops has been around for some time now. It offers great opportunities to reduce IPv4 address usage in the distribution and access layer, and enables providing IPv4 as a pure add-on, keeping a clean IPv6 address structure underneath. Despite its benefits, major challenges for deploying IPv4-with-IPv6 next-hops in practice persist. While, e.g., BGP supports such routes using RFC8950, many other IGPs still lack support. Other major issues are 'the last mile', i.e., auto-configuring clients (or, for this use-case, more likely servers), and the impact of IPv4-with-IPv6 next-hop usage on traceroutes. In this talk, we will go over some current developments in these areas, which should make IPv4-with-IPv6 next-hops a viable option for practical deployments in the coming years. We will also expand further on possible deployment scenarios, where IPv4-with-IPv6 next-hops can remove further legacy Layer-2 infrastructure, e.g., LACP. What actually changes in your network when you stop treating IPv4 as infrastructure and start treating it as a service? draft-vanmook-intarea-ipv6-resolved-gateway (presented at IETF 126, WG adoption call pending) defines a single sentinel gateway address, provisionally 192.0.0.11 (requested from the IANA Special-Purpose Registry, not yet assigned), handed out as the ordinary DHCPv4 default gateway. Updated hosts resolve their first hop from the IPv6 neighbour cache; unmodified hosts ARP for the sentinel once and the router answers. That's the whole mechanism. Everything downstream of it is the interesting part. This talk is about what that does to a running network: no IPv4 subnets anywhere, no ARP, no FHRP, IPv4 address pools that go flat — any /32 works anywhere in the footprint, nothing stranded by subnet sizing. The core forwards v4-via-v6 (RFC 8950) with no IPv4 configured on any router interface. On the implementation side: host implementations for Linux (userspace daemon and native systemd-networkd), FreeBSD, macOS and Windows, with prebuilt packages; a namespace conformance lab with a zero-ARP assertion; verified unmodified-host behaviour across seven operating systems; and vendor configuration examples for IOS XR, JunOS, SR OS, EOS and RouterOS. On the router side, three working deployment models: a single-gateway reference, an active/active anycast VRRP pair, and a BGP-orchestrated multi-gateway fabric — fungible gateways, host /32s injected from inventory, and the entire DHCPv4 path carried as IPv4 values over IPv6 next-hops, with no IPv4 management network at all. Plus the failure modes, the ND health prerequisites, and what breaks when you get it wrong. No tunnels. No translation. No flag day. Keep the shape, change what it means. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/V7Y3X9/

Video:denog18-a-99-eng-IPv4_as_a_service_on_an_IPv6-only_network_hd.mp4

November 15, 2026 11:00 PM

Teach Networking!? (denog18)

There are many ways for career starters to get into IT: apprenticeships, university degrees, dual study programs, or through self-study. But how do they learn networking and IT infrastructure? With this lightning talk, I’d like to inspire you to teach young people how networking works! What are the most difficult topics to explain? What about practical experience? I've been teaching the basics of networking for several years now, and I'd like to share my experience with you. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/E7UDUC/

Video:denog18-a-94-eng-Teach_Networking_hd.mp4

November 15, 2026 11:00 PM

IPv6 routing loops -- A call to fix router configurations. (denog18)

Routing loops and the amplification of looping packets are known problems on the IPv6 Internet. In a recent measurement study, we found that both problems are still present, potentially harming Internet stability. Although routing loops are often easy to fix, they receive limited attention from the network operator community. Since 2025, we aim to raise awareness of routing loops and amplification at network operator events. In 2026, we started to weekly measure the deployment of routing loops and amplifications on the IPv6 Internet. In this talk, we present how community outreach has helped significantly reduce the impact of these network misconfigurations. We further provide an update on the current state of these issues on the IPv6 Internet with a particular focus on the RIPE and DE region. We hope these misconfigurations will eventually disappear and encourage the DENOG community to spread the word, check their networks, and help eliminate routing loops from the IPv6 Internet. Until then, we will continue measuring, reporting, and raising awareness. To assist in resolving these problems, we have made our findings publicly available at https://ipv6-sra.realmv6.org/routingloops, allowing operators to check whether their networks are affected by routing loops. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/PRRFUN/

Video:denog18-a-85-eng-IPv6_routing_loops_--_A_call_to_fix_router_configurations_hd.mp4

November 15, 2026 11:00 PM

ICMP trickery in "reduced-IPv4" networks (denog18)

Did you think IPv6 transition technologies were too easy? "one more" wasn't enough choices? Did you ever have to debug one of these "simple" setups? Come join for a walk through ICMP (v4 and v6) behavior and features! This presentation will go through the various edge cases and overlaps between ICMPv4 and ICMPv6 in transition/IPv4 phase-out setups. One of these is likely applicable to most of us — hopefully you're not a poor soul for whom _all_ apply! A rough outline: - RFC 4884 and historic context: ICMP in MPLS networks - convincing your tools to not hide the goods from you - ICMP translation in NAT64 devices - midpath ICMPv6 into NAT64 - 192.0.0.8 is love, 192.0.0.8 is life - ICMPv4 on RFC 8950 devices - Good thing nobody needs PMTUD, right? Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/ZQEANK/

Video:denog18-a-84-eng-ICMP_trickery_in_reduced-IPv4_networks_hd.mp4

November 15, 2026 11:00 PM

QoE-riosities of 2026 - What we saw on the Internet this year (denog18)

While everyone talked about the DENIC outage this year, we monitored the critical stuff higher up the stack. The football world championship was a challenge for streamers and network operators. So, how did they actually perform under pressure? Beyond live events, we put different access technologies to the test in our lab to analyze how factors like latency, jitter, and bandwidth caps directly impact Quality of Experience (QoE) on the web and beyond. Let's have a data-driven look at the Unexpected of 2026. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/ZCXTKW/

Video:denog18-a-68-eng-QoE-riosities_of_2026_-_What_we_saw_on_the_Internet_this_year_hd.mp4

November 15, 2026 11:00 PM

Retrofitting API into a routing software (denog18)

Configuring a router via text CLI and configuration file editing is not very 2026. In BIRD, we are trying to catch the departing train and implement a CORECONF variant of an IETF-standardized YANG-based API. We've created a prototype but getting things right is harder than it seems. This is a report on what has already gone wrong and what is expected to fail in the future. While a standardized API looks simple on surface, the reality is much more convoluted. There are three standards for communication, NETCONF, RESTCONF and emerging CORECONF, each of these with slightly different semantics. Lots of the YANG modules are not yet finalized and implementation specifics are leaking into them from their authors. In the best case, we end up with the implementations slightly differing in what is implemented, and being mostly compatible for automated access. Yet, the actual future may be much more dire, with the users having to cater for three different protocols and vastly diverse implementation status of the standardized API. All of that is spiced up by performance challenges. With BIRD, we are kinda late to the party. Everybody has some API working. That brings a disadvantage on the market, but it also allows us to study the previous attempts, see possible problems and implement our API to our standards, including high performance and stability. We can also see emerging compatibility issues and there are some attempts to develop proxies and convertors to bridge the gaps. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/3BJJKY/

Video:denog18-a-51-eng-Retrofitting_API_into_a_routing_software_hd.mp4

November 15, 2026 11:00 PM

EVPN - One Control Plane to Rule Them All (denog18)

Modern service provider networks are evolving rapidly: transports like VXLAN, MPLS, Segment Routing and SRv6 are being used while many legacy control plane protocols are still in operation. This often results in unnecessary complexity, multiple signalling mechanisms and operational overhead. In this talk, I’ll explore how BGP EVPN has evolved into a transport-agnostic control plane capable of unifying services across MPLS, VXLAN, SR, and SRv6. The goal is simple: move away from fragmented legacy protocols and toward a single, scalable control plane for L2 and L3 services. We’ll look at recent EVPN innovations and discuss how service providers can benefit from simplifying their architectures while preparing their networks for future transport technologies. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/VCQLXW/

Video:denog18-a-45-eng-EVPN_-_One_Control_Plane_to_Rule_Them_All_hd.mp4

November 15, 2026 11:00 PM

Day 1 Closing (denog18)

That's a wrap on Day1, time for the social! Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/EQ7KVJ/

Video:denog18-a-106-eng-Day_1_Closing_hd.mp4

November 15, 2026 11:00 PM

DENOG18 Opening (denog18)

Welcome to DENOG18! Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/UB3PVV/

Video:denog18-a-104-eng-DENOG18_Opening_hd.mp4

November 15, 2026 11:00 PM

Ethernet Won Inside the AI Data Center. Can It Cross an Operator Boundary? (denog18)

Inference is quietly overtaking training as the dominant AI workload, and unlike training — concentrated in a handful of hyperscale halls — inference wants to sit close to users, pulling AI capacity into distributed sites across Europe. The industry has spent the last two years re-engineering Ethernet (via the Ultra Ethernet Consortium and platforms like NVIDIA Spectrum-X) to match InfiniBand's performance for exactly this kind of workload, and now even ships Ethernet fabrics purpose-built to stitch multiple physical data centers into one logical AI factory. That's a solved problem when one company owns every site. This talk asks what happens when it isn't — when distributed inference has to span operators, jurisdictions, and ownership boundaries — and what a federated, policy-aware Ethernet fabric for that world would need to look like. Ethernet is rapidly becoming the preferred back-end network for AI infrastructure. Technologies such as RoCE, Ultra Ethernet, NVIDIA Spectrum-X, and emerging “scale-across” architectures promise predictable, high-performance connectivity within and between AI data centers. These architectures generally make one important assumption: a single organization controls the servers, switches, telemetry, congestion policies, and inter-site connectivity. Under that model, several physical data centers can be engineered to behave as one logical AI environment. Distributed European AI infrastructure may not have that luxury. Inference capacity will increasingly be deployed across hyperscalers, regional clouds, colocation facilities, metro-edge sites, and specialist GPU providers. The networks connecting those sites may also belong to different fiber and connectivity operators. Each participant controls only part of the infrastructure, exposes limited operational information, and may operate under different commercial and jurisdictional requirements. This creates a question that faster Ethernet alone cannot answer: what happens when an AI fabric reaches an operator boundary? The talk begins by separating two ideas that are frequently conflated. Distributed AI services can steer requests between independent sites without extending a tightly coupled GPU fabric between them. Some workloads, however, including model distribution, distributed inference, resilience between GPU sites, and certain forms of model parallelism, place much stronger demands on inter-site connectivity. We will examine which workloads genuinely benefit from network-level federation and which should remain distributed at the application layer. We will then look at what changes when traffic crosses a network-to-network interface. Can congestion-control assumptions survive between independently operated domains? What latency, loss, and bandwidth guarantees are technically credible? How can operators exchange useful telemetry without exposing internal topology? Who selects the end-to-end path, who responds to failures, and how can customers verify that the delivered service matches what was promised? Sovereignty adds another dimension to this problem. A sovereign AI service is not defined solely by the location of its GPUs. Customers may also care about where their traffic travels, who owns and operates the infrastructure, which jurisdictions can exercise control over it, where encryption keys are held, and whether those claims can be independently verified. Consequently, path selection may need to consider geography, jurisdiction, operator identity, and operational control alongside conventional performance metrics. The talk proposes a candidate architecture based on coordinated path computation with domain-local enforcement. Each operator retains control of its own network while exposing an abstract set of capabilities such as latency class, available bandwidth, path diversity, geographic scope, and jurisdictional attributes to a higher-level coordinator. The coordinator requests an outcome rather than configuring another operator’s network, while end-to-end measurement verifies whether the resulting service meets its performance and sovereignty objectives. We will test this architecture against the timing and congestion requirements of GPU networking and identify where conventional carrier federation begins to fail. The goal is not to claim that a continent-wide lossless Ethernet fabric is immediately practical. It is to determine which multi-operator AI connectivity services are feasible, which workloads they can support, and which technical assumptions still require new standards or experimentation. Attendees will leave with: - A clear distinction between distributed inference services and distributed GPU fabrics. - An understanding of what breaks when AI traffic crosses an operator boundary. - A practical definition of sovereignty covering compute, connectivity, control, and verification. - A candidate model for policy-aware, multi-operator AI connectivity. - A framework for identifying which AI workloads can realistically operate across federated networks. The commercial opportunity for operators may not be “one enormous Ethernet fabric.” It may instead be something more achievable: verifiable, policy-aware connectivity between AI-capable sites, with measurable performance, geographic, jurisdictional, and operational guarantees. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/73Q8NL/

Video:denog18-90-eng-Ethernet_Won_Inside_the_AI_Data_Center_Can_It_Cross_an_Operator_Boundary_hd.mp4

November 15, 2026 11:00 PM

Geoinformation Systems & Internet Infrastructure (denog18)

KML, KMZ, DXF - hat wahrscheinlich schon jede:r mal in der Hand gehabt, nach dem man redundante Leitungen bestellt hat. Aber was macht man eigentlich sinnvolles damit? KML, KMZ, DXF - everyone knows or used those file formats, at least after asking the carrier where the redundant circuits are. But is there anything useful you can do with those files? Geoinformationsdaten sind eine der Grundlagen für stabil funktionierende Infrastruktur. Egal ob Glasfasern im Boden, Glasfasern an Hochspannungsmasten oder Richtfunkstrecken. Wie funktioniert die Trassenplanung- und Instandhaltung, und welche Vorteile habe ich als Nutzer:in um meinen Netz zu verstehen und den Netzbetrieb zu optimieren? Geo information data are the basis for reliable infrastructure. Not only for fiber in the ground, but even fiber on power lines or microwave links are planned this way. How does the planning of new fiber routes and their maintenance work, and which benefits do I get from geo data for my own network? Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/97DCW3/

Video:denog18-61-eng-Geoinformation_Systems_Internet_Infrastructure_hd.mp4

November 15, 2026 11:00 PM

IPv6 in firmware: Still booting in the wrong decade (denog18)

Every server depends on firmware to boot and most also rely on firmware for remote management. U-Boot, EDK2 (UEFI), OpenBMC, you name it. And they all share the same issue: IPv6 support ranges from half-baked to non-existent. Why is this still the case in 2026? In this talk I'll go into two areas of server firmware that operatores rarely look at closely: the one that boots the server, and the one that allows out-of-band management via the Baseboard Management Controller (BMC). On the boot side: Do PXE and HTTP boot actually work over IPv6? And what unexpected side effects do you might see? On the management side: How does IPv6 support look on a BMC today, and what's still broken? Nobody's going to fix what nobody complains about. Let's find out how broken this is and what we can do about it. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/XPH3W7/

Video:denog18-54-eng-IPv6_in_firmware_Still_booting_in_the_wrong_decade_hd.mp4

November 15, 2026 11:00 PM

Modular Nokia SR OS automation from scratch (denog18)

Existing automation solutions are usually monolithic and require you to migrate all of your existing infrastructure at once to the automation. I wanted to introduce automation step by step and wanted to continue to use our existing sources of truth. So I have built a modular automation solution that allows us to build a completely separated automation module for everything we want to automate in our network. Existing automation solutions are usually monolithic and require you to migrate all of your existing infrastructure at once to the automation. But I wanted to continue using our existing sources of truth and wanted to introduce automation in our network step by step and not in one big step. Additionally, there is the security perspective: do you really want to grant an automation solution that you don't fully understand internally unrestricted access to all of your routers? The solution: modular network automation from scratch: write a module for any aspect you want to automate in your network. Want to automate your peerings with Peering-Manager? Write a module for it. Want to automate your base router interfaces with NetBox? Write a module for it. The modules itself are isolated from each other in the configuration by using one config group for each module (basically a separate config tree for each module). This by design eliminates the possibility of collisions between modules and makes consecutive deployments easier by fully replacing the config group on each run. It additionally allows you to minimize the permissions of an automation user to the absolute required minimum by only granting them access to the config group. Furthermore, the use of config groups allows you to override the automation on any given time in the main config tree or even exclude some parts of the main config tree from it. Although this solution was developed for Nokia SR OS, it can in principle be extended to any platform that is transactional and supports something like config groups. Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/KPYWEU/

Video:denog18-50-eng-Modular_Nokia_SR_OS_automation_from_scratch_hd.mp4

November 15, 2026 11:00 PM

Newcomer Sessions (denog18)

Welcome to your first DENOG conference. In this session, we will guide you through the community, the event and everything DENOG! Licensed to the public under http://creativecommons.org/licenses/by/4.0 about this event: https://cfp.denog.de/denog18/talk/AVHF39/

Video:denog18-109-eng-Newcomer_Sessions_hd.mp4

November 15, 2026 11:00 PM

Metalab

CCC Duesseldorf

Wochenrückblick (Woche 46/2026)

Diese Woche im Chaosdorf? Stein, Schere, Papier.

Stein

Unser Dorf soll schöner werden! Deshalb fiel der Startschuss für den Umbau der Cave, mit mehr Stauraum und demnächst frisch aufgeräumt und neu aufgebaut. Danke an alle, die hier mithelfen!

Weißer Schrank mit 9 quadratischen Fächern, in etwas Schulterhöhe, aufgenommen in der Cave.

Schere

Aufnahme unseres alten Home Assistant Dashboards auf dem Touch-Bildschirm im Hackcenter.

Und das Dorf bekommt nicht nur in der Cave ein Update, sondern auch in der Infrastruktur. Unser bestehender Home Assistant hat über die Jahre viele Basteleien und coole Projekte gesammelt, und ist dabei leider ein bisschen langsam und unzuverlässig geworden. Vor allem unsere Zigbee-Geräte sind mit dem aktuellen Setup etwas unglücklich, deshalb setzen wir hier die Schere bei den alten Zöpfen an und setzen das mal eben neu auf. Das braucht viel Liebe und noch viel mehr Zeit, aber Andromeda, maximemelian, neintonine, und ich haben dann doch an einem Tag schon so 90% umsetzen können. 🎉

Papier

In eigener Sache: Den Chaosdorf-Wochenrückblick gibt es jetzt auch per Fax (im EPVPN)! Über Faxabruf könnt ihr unter der 3889 ein Abo-Formular anfragen, und bekommt dann immer ein Fax, wenn es etwas neues im Chaosdorf-Blog gibt.

Bild des Fax-Abo-Formulars in Nahaufnahme, mit dem Faxgerät im Hintergrund.

by cyaniccerulean at November 15, 2026 02:00 PM

Metalab